Financial Services
Verify continuously. Contain the blast radius. Prove your policy controls.
Financial institutions carry risk they do not directly control. Concentrated SaaS dependencies, compromised suppliers, insecure vendor defaults, and blurred boundaries between third-party services and internal systems all widen exposure. The business consequence is operational: a single supplier or connected asset can interrupt payment processing, branch operations, and trading services, and every one of those interruptions has to be explained to examiners.
Forescout reduces that exposure by validating trust continuously across users, devices, contractors, and partners, containing failures so they stay local, and recording every access decision as audit and investigative evidence.
Universal Zero Trust Network Access and Forescout
Universal ZTNA extends continuous access decisions beyond managed users and laptops to everything else connected to the institution: unmanaged endpoints, contractor and partner devices, IoT, OT, and the cyber-physical systems that sit outside traditional security tooling, across campus, cloud, and remote locations.
The Forescout Vistaro platform delivers that coverage without requiring an endpoint agent for discovery, assessment, and monitoring. Devices that cannot accept software, and devices you do not own, are still identified, evaluated, and governed by policy.
Business outcomes with Forescout Vistaro AI

Reduce exposure you inherit from third parties
Shared SaaS platforms, managed service providers, or connected vendors create one path into many systems at once. Continuous verification and least-privilege access keep that path from creating an institution-wide compromise.

Keep disruption local when something fails
Segmentation across campus, cloud, and remote locations limits how far any single compromise travels, and extends security policy to ATMs, physical security systems, and building management.

Shorten the time between leading risk indicators and response
Automated workflows across EDR, SIEM, SOAR, firewalls, CMDBs, and threat intelligence convert platform observation into automated enforcement.

Prove that policy is enforced, not just written
Comprehensive logging covers authentication requests, authorization decisions, posture assessments, and network movements, supporting requirements for DORA, FINRA, GLBA, PCI DSS, SOX, SWIFT, GDPR, and other applicable regulations.
Why Forescout for Financial Services?
The Forescout Vistaro™ platform enables Universal Zero Trust Network Access, continuously validating trust across users, devices, applications, and connected banking infrastructure. The platform delivers agentless security that identifies and assesses every connected device, prioritizes risk remediation, detects threats, and enforces compliance and response workflows across banking, payment, and trading environments.

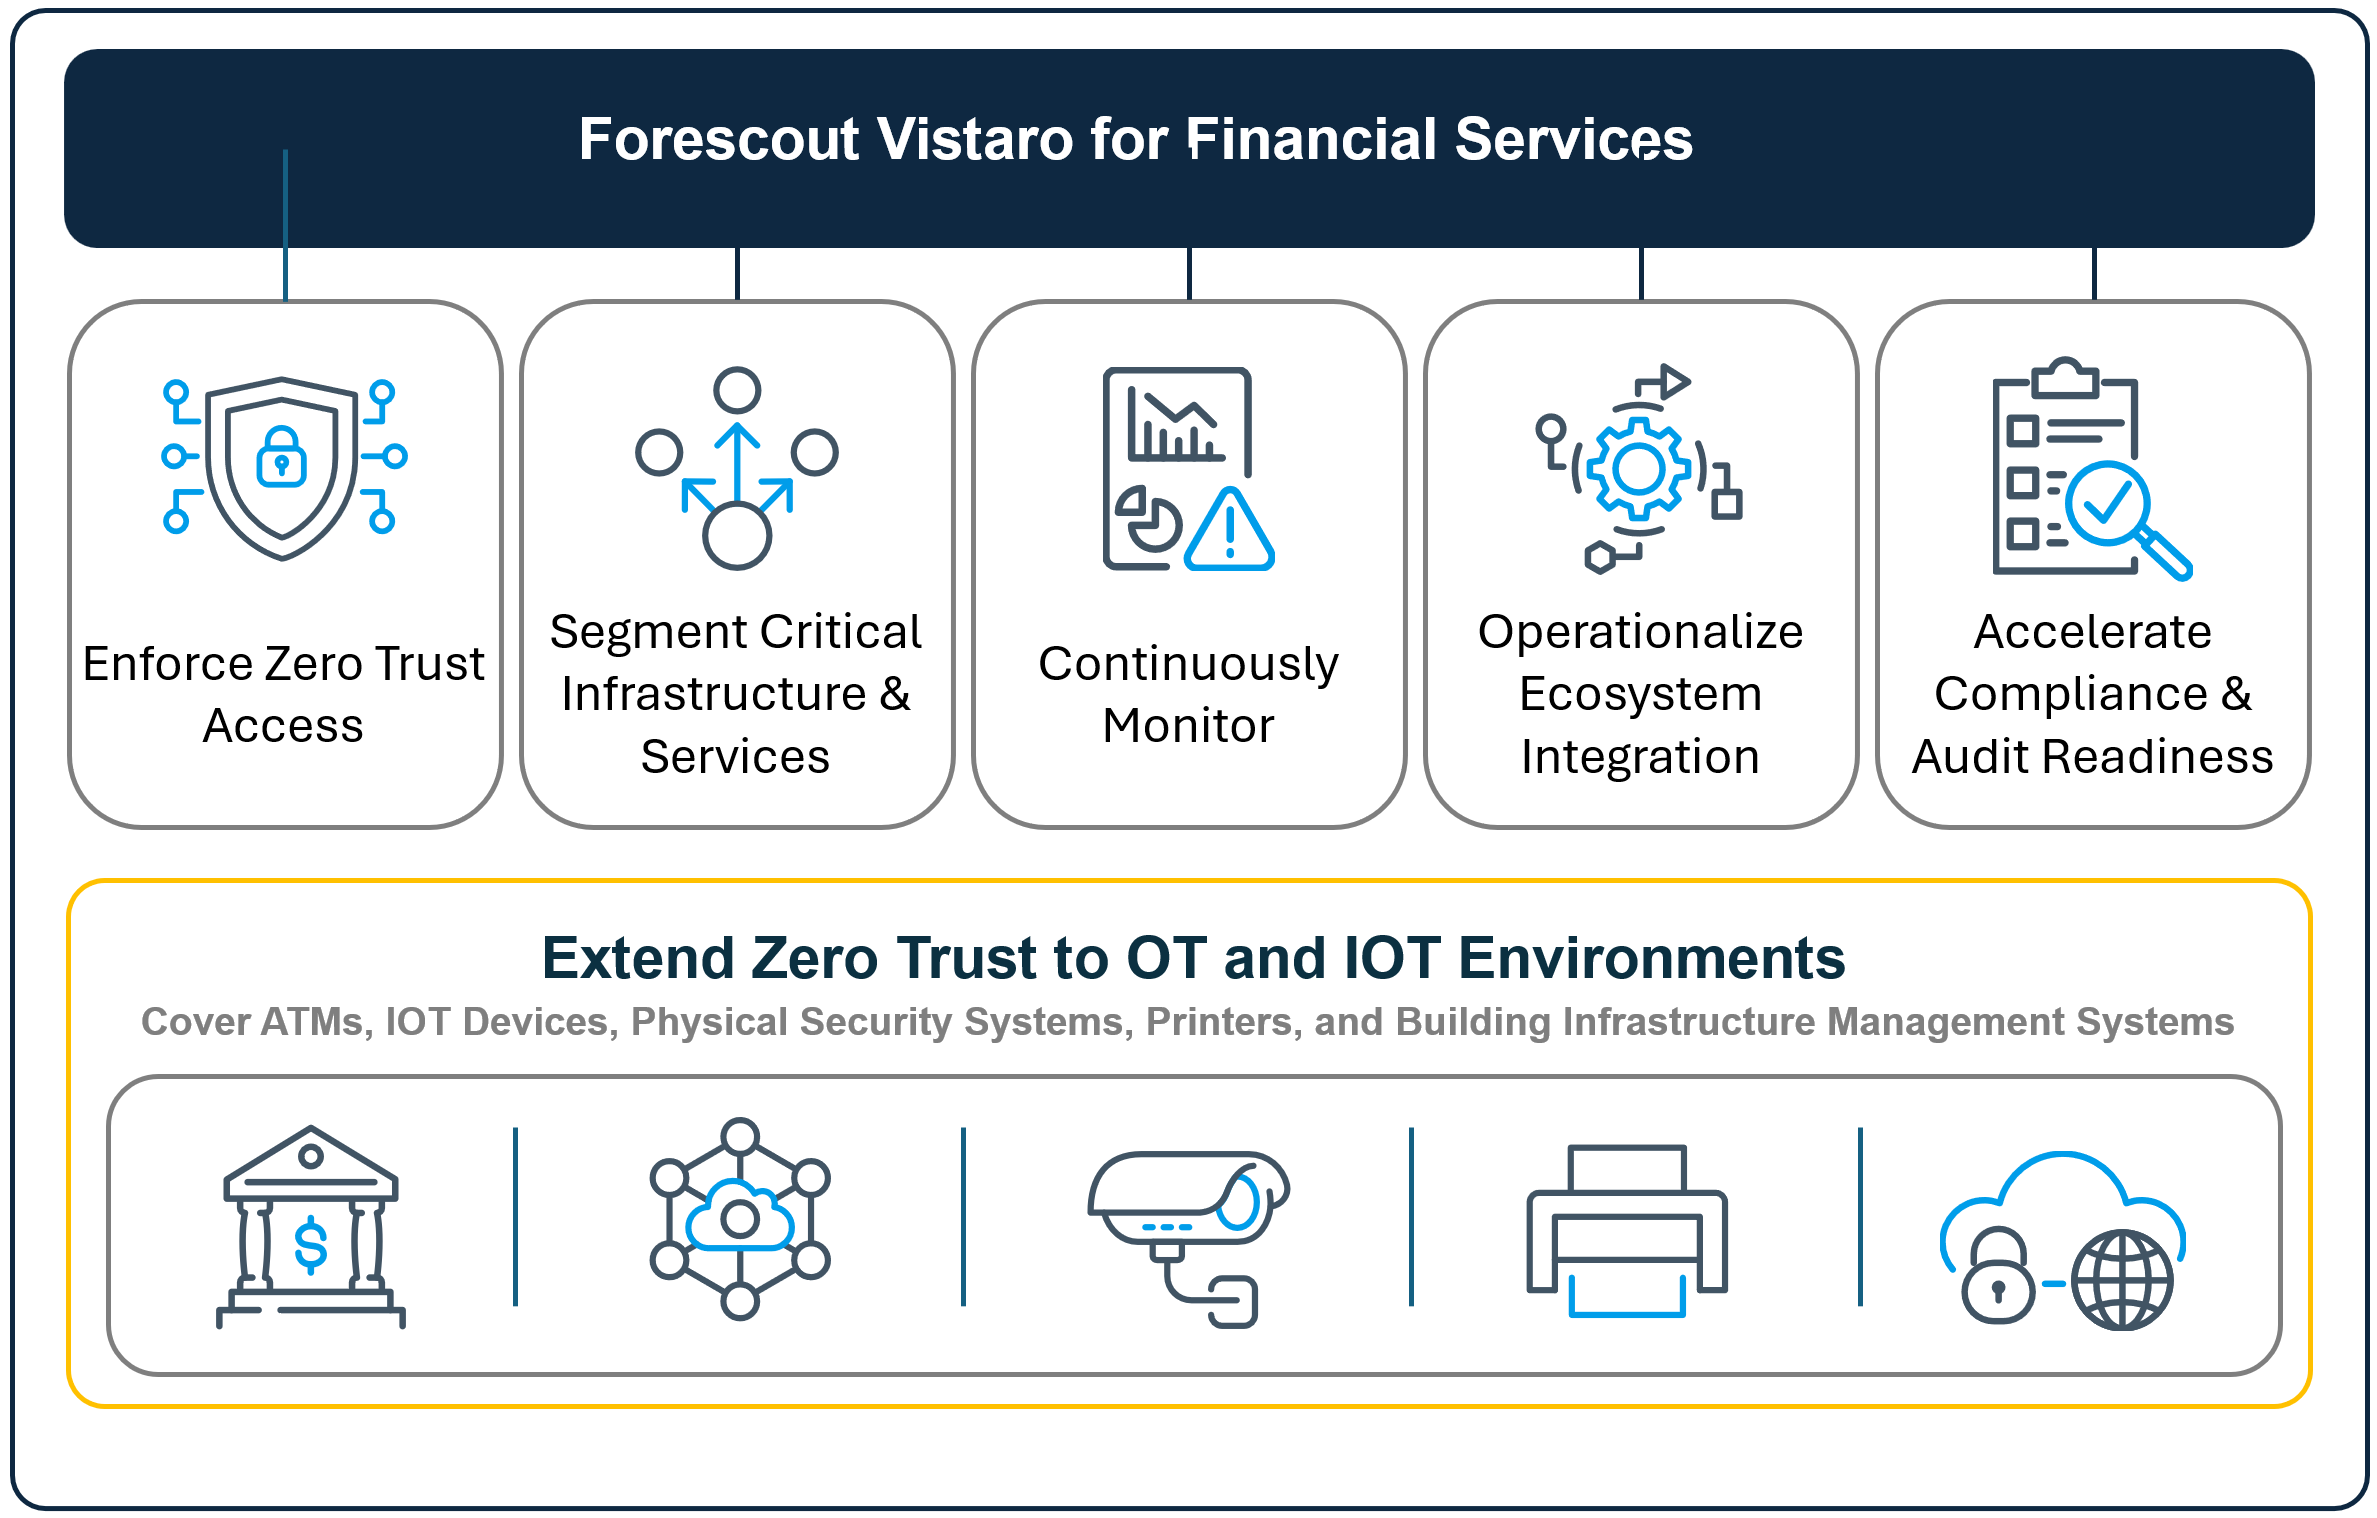
Enforce Zero Trust access across every connected asset
Only authorized, compliant devices gain access.
Protect critical financial infrastructure through dynamic segmentation
Reduce the risk of lateral movement and ransomware with unified, continuous enforcement of least-privilege access policies across campus, cloud, and remote locations.
Continuously monitor device health and security posture
Surface noncompliant devices, configuration drift, and suspicious behavioral changes in real time.
Extend Zero Trust to IoT and OT environments
Cover ATMs, IoT devices, physical security systems, printers, and building management infrastructure.
Operationalize security through integrated ecosystem automation
Automate workflows across EDR, SIEM, SOAR, firewalls, CMDBs, and threat intelligence platforms
Accelerate regulatory compliance and audit readiness
Automate control enforcement and evidence collection for FINRA, GLBA, PCI DSS, SOX, SWIFT, GDPR and other regulations.

Flexible. Versatile. Rapid Deployment.
Forescout offers unmatched deployment flexibility to meet the diverse hardware and cloud requirements of modern environments. We ensure compatibility with existing infrastructures while minimizing operational disruption. This versatility makes it an ideal choice for your organization. If you seek robust, scalable solutions tailored to your unique operational and regulatory landscapes, look no further.
The Forescout Vistaro™ platform adapts seamlessly with options for on-premises installations, virtual machines and Docker-based containerized deployments, including:
- Air-gapped systems for high-security needs
- Forescout appliances that deliver maximum visibility and control
- Hybrid configurations to connect distributed sites
- Fully cloud-based operations for scalability
…and Sensors that can be deployed as:
- Standalone appliances
- Installed directly on routers and switches for quick implementation without production disruption
- Or configured as active sensors to query network infrastructure
Deploy Forescout on Phoenix Contact Security Solutions Industrial Switching Platform for enhanced security and simplified deployments
Reduce physical hardware and deploy Forescout in Azure – a scalable, robust and cost-effective solution
Deploy Forescout on Keysight packet brokers for efficient and scalable deployments

Leverage the Dell Validated Design for Energy Edge to deploy in substations with ABB and Forescout
Related Solutions


See Forescout in Action
Choose Your Demo Experience
Self-Guided Demo
Take a self-guided demo for a live, hands-on experience
- Interactive product tour
- Explore key features
- Go at your own pace
or
Custom Demo
Get a personalized tour of our solutions and see how we can help you automate cybersecurity.
- Live demo with expert
- Tailored to your use case
- Get your questions answered