Forescout Research –
Vedere Labs
“Vedere” is the Italian word meaning “to see,” which epitomizes the mission of Forescout Vedere Labs, the cybersecurity research arm of Forescout. Our team of global experts focuses on increasing visibility of cybersecurity threats and vulnerabilities for all connected asset types and providing mitigation steps organizations can use to protect themselves.
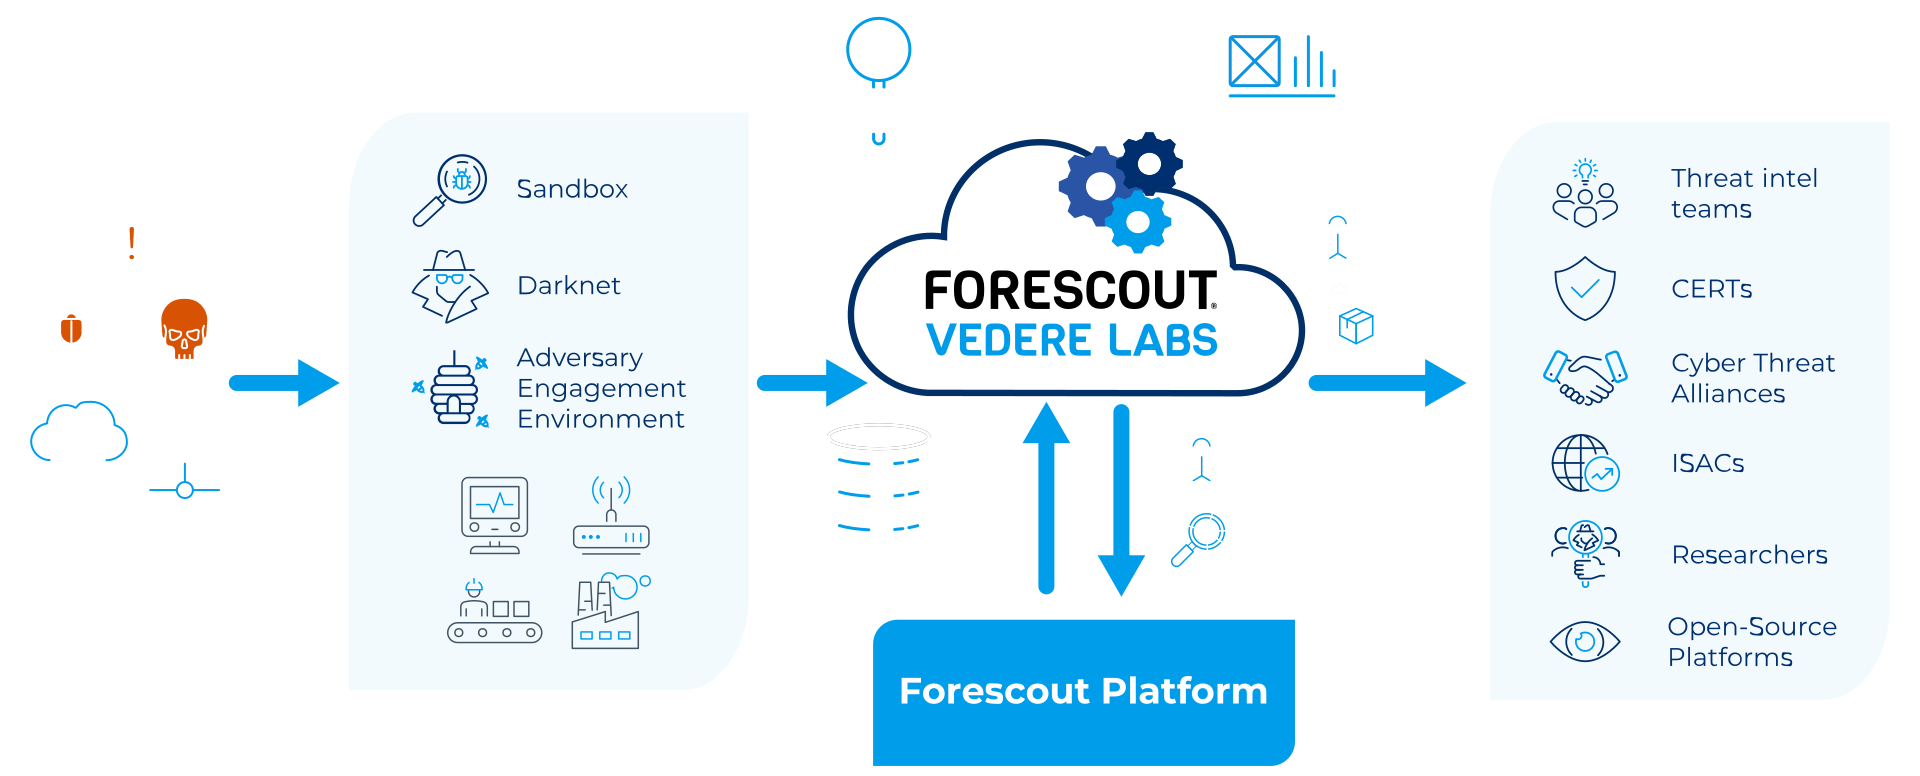
Our research is fed into the Forescout Platform and shared with the cybersecurity community, including CISA and other cybersecurity agencies, CERTs, ISACs, open-source projects, device manufacturers, universities and other researchers.
What We Do
Vulnerability Research
- Focus on vulnerabilities against managed and unmanaged devices (IT/IoT/IoMT/OT)
- 200+ vulnerabilities discovered in last 5 years
- 100+ known exploited vulnerabilities on unmanaged devices
Threat Reports
- Manual and automatic analysis of malware samples collected via customer telemetry and other sources
Threat Intelligence & Detection
- Daily context-rich, machine-consumable threat feeds
- Detection rules to keep our Threat Detection & Response solution on top of emerging threats
- Live dashboards
How We Do It
Forescout Vedere Labs studies what attackers are working towards by observing actual attacks in our sandboxes, on the Darknet and in our Adversary Engagement Environment. We analyze significant attacks and generate vulnerability and threat intelligence that is consumed by the Forescout Platform. We also create corresponding detection rules that are added to Forescout Threat Detection & Response to help ensure customers can protect their IT, OT, IoT and IoMT environments.
Firsthand Observations in Our Research Laboratory
Located in Eindhoven, Netherlands, our research laboratory is where we observe firsthand the vulnerabilities being exploited and attacks in progress. The information we collect is analyzed to generate threat intelligence, calculate multifactor risk scores and create detection rules.
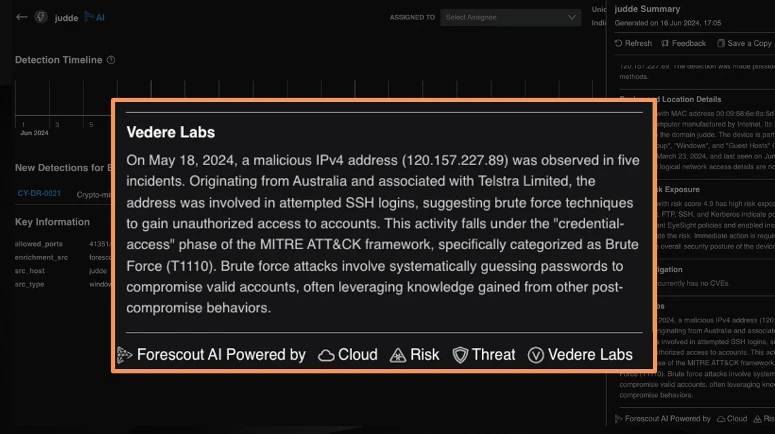
How Vedere Labs Uses Artificial Intelligence
VL threat intelligence is integrated on generative AI products, such as Microsoft Copilot for Security, allowing security analysts to query OT and IoT-specific threat intelligence directly from Forescout Research.
We also have integrated generative AI within our TDR solution, which summarizes proprietary intelligence that can be gathered about IP addresses and other indicators of compromises observed during an incident.
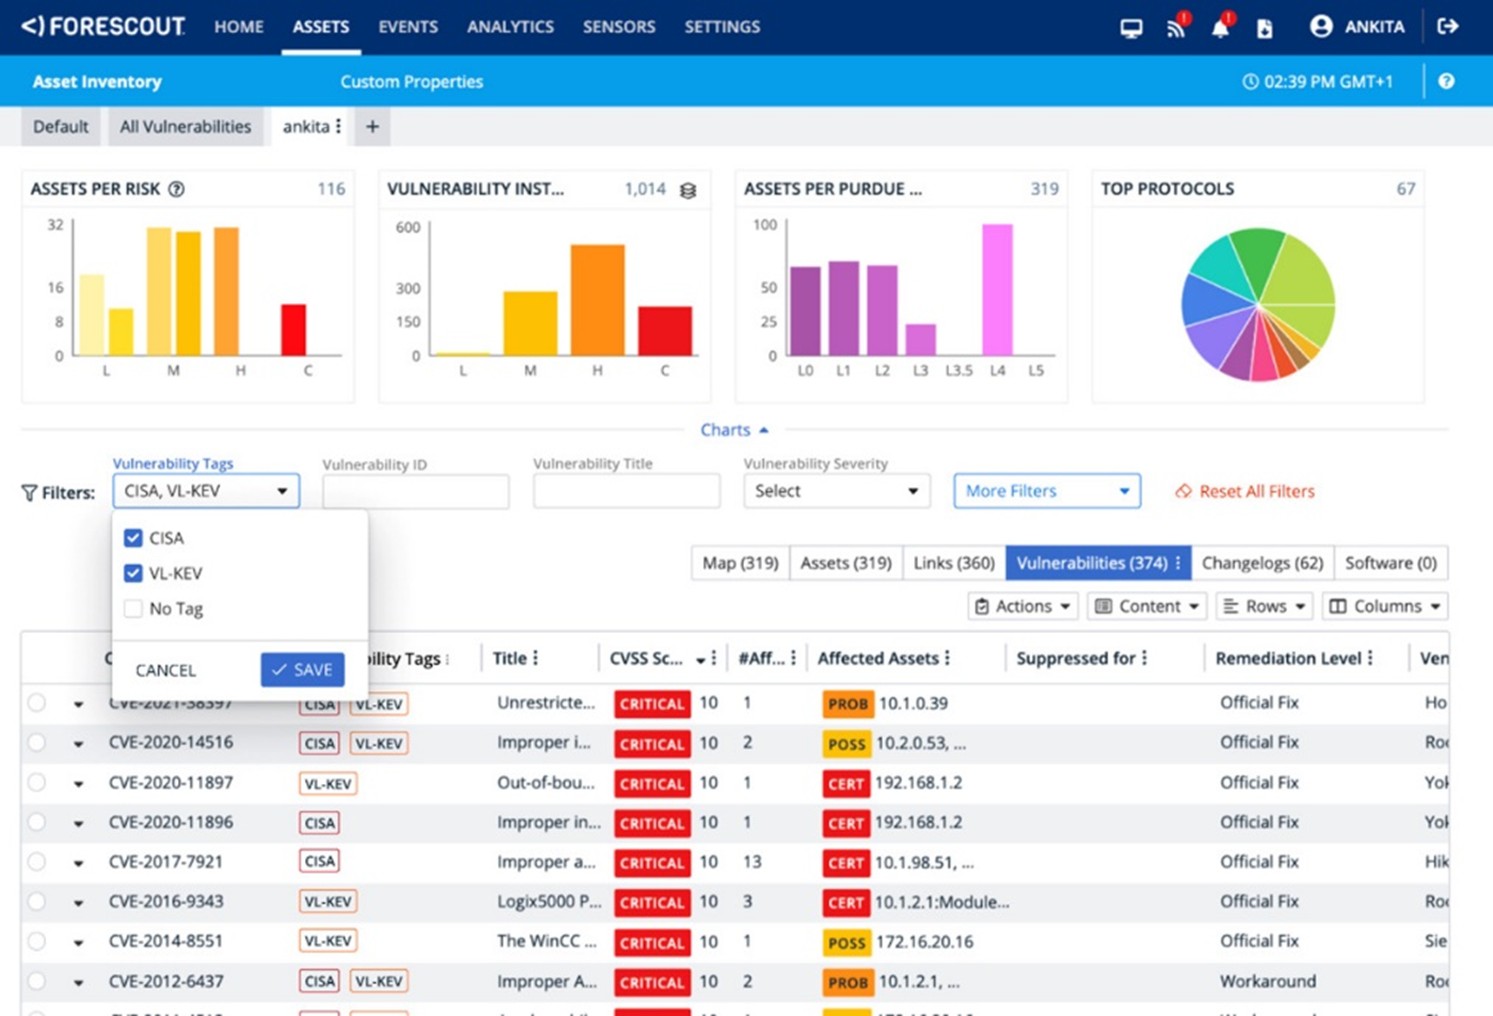
VL KEV: Our Proprietary List of Vulnerabilities
Our KEV list is compiled from real attacks we observe within our OT and IoT-specific honeypots, customer data and third-party intelligence. The list is complementary to industry-standard sources, such as CISA KEV. It is updated in tandem with other threat intelligence for Forescout eyeInspect and REM solutions. This type of intelligence allows users to prioritize vulnerability management actions based on what is currently being exploited by threat actors.
Partnerships and Threat Intelligence Sharing Groups
Vedere Labs is a proud member and contributor to threat intelligence sharing groups, including CERTs, cyber threat alliances and ISACs — where new intelligence and best practices are shared. Member organizations include industry, academia and governments where we share machine-readable intelligence and human-readable reports.
European Energy ISAC
Forescout is a founding member and actively participates in the threat intelligence task force.
ETHOS
Forescout is a founding member and part of the board of directors in this industry partnership dedicated to OT-centric, open-source sharing of anonymous early-warning threat information.
OT-ISAC
Forescout is a partner that shares reports, answers questions about emerging threats and presents at conferences and threat briefing meetings.
CISA JCDC and AIS
Forescout shares indicators of compromise and reports distributed to other members of the JCDC and IAS initiatives.
ACSC CTIS
Forescout shares indicators of compromise and reports distributed to other members of the CTIS initiative.
Data. Lots of Data.
The threat intelligence data we analyze comes from millions of connected devices that we monitor that give us billions of data points about device configuration and network behavior. It also comes from attacks we observe and dissect and other sources that we monitor.
Devices
- 19 million monitored devices
- 39 billion unique data points
- 1,500 global sites
- 6,500+ unique vendors
- 2,300+ unique OS versions
Threats
- 750+ threat actors
- 100+ ransomware group leak sites
- 20+ C2 types monitored on the Internet
- Third-party intel
Forescout Research - Vedere Labs Featured In...
Researchers uncover software flaws leaving medical devices vulnerable to hackers
Researchers say they have found more than a dozen vulnerabilities in software used in medical devices and machinery used in other industries that, if exploited by a hacker, could cause critical equipment such as patient monitors to crash…
Read More
Critical Bugs Expose Hundreds of Thousands of Medical Devices and ATMs
“You can imagine the type of impact an attacker could have when they can either exfiltrate data from medical equipment or other sensitive devices, potentially tamper with lab results, make critical devices unavailable, or take them over entirely…”
Read More
Government cyber workers increasingly concerned hackers will strike during shutdown
The government’s cybersecurity professionals are increasingly concerned that hackers will take advantage of the partial shutdown to tamper with sensitive government data or steal citizens’ information — and that the bare-bones staff won’t be able to fend them off…
Learn More
OT:ICEFALL FINALE
Forescout Vedere Labs is wrapping up its yearlong project looking at design vulnerabilities in operational technology with a closing report today that blames many of the issues they’ve encountered on vendors of the technology not implementing designs that would build security into the systems…
Read More
Dray:Break
In 2024, routers are a primary target for cybercriminals and state-sponsored attackers – and are the riskiest device category on networks. We investigated one hardware vendor, DrayTek, with a history of security flaws to help it address its issues and prevent new attacks — especially when ransomware and denial of service attacks are so high today.
Forescout Research. In Your Inbox. Every Month
With 13 cyber attacks every second, it’s hard to keep up.
To help, Vedere Labs now has its own newsletter. Curated by our research leaders, you’ll receive the most crucial information you need to stay ahead of attackers.
It’s loaded with useful context, links and spotlights on threat actors, newly exploited vulnerabilities and other must-know asset intelligence. Once a month. Nice and easy.
Meet Our Leader
Daniel dos Santos
Daniel dos Santos is the Head of Research at Forescout Vedere Labs, where he leads a team of researchers that identifies new vulnerabilities and monitors active threats. He holds a PhD in computer science, has published over 35 peer-reviewed papers, has found or disclosed hundreds of CVEs — and is a frequent speaker at security conferences.
Explore Vedere Labs Blogs
-
Forescout Wins Best IoT Security Solution Provider of the Year
We are thrilled to announce Forescout has been named the winner of the “Overall IoT Security Solution Provider of the Year” award in the fifth annual CyberSecurity Breakthrough Awards. The awards program is conducted by CyberSecurity Breakthrough, a leading independent market intelligence organization, and aims to honor excellence and recognize innovation, hard work and success […]
Read More -
Forescout Accelerates Organizations’ Path to Zero Trust with Expanded Network Segmentation Capabilities
Network segmentation has become a valuable tool to protect data and manage the attack surface during any cybersecurity incidents. It’s also a critical component of Zero Trust programs and organizations’ ability to maintain compliance amid numerous regulations being introduced by governments and industry bodies. Yet, enterprises should not hesitate when it comes to implementing network […]
Read More -
A Roadmap to Implement Enhanced Security Measures for “Critical Software”: How to Comply with OMB’s Memo for Federal Civilian Agencies
On August 10, the Office of Management and Budget (OMB) released guidance to civilian agencies on how to implement the goals of the May 12 Executive Order on Improving the Nation’s Cybersecurity with regard to software that is considered “critical.” Agencies have just 60 days to identify “critical software” and 1 year to implement enhanced […]
Read More -
New Critical Operational Technology Vulnerabilities Found on NicheStack – Mitigation Advised
Forescout Research Labs and JFrog Security Research have discovered a set of 14 new vulnerabilities affecting the NicheStack TCP/IP stack, which we are collectively calling INFRA:HALT. The new vulnerabilities allow for remote code execution, denial of service, information leak, TCP spoofing, or DNS cache poisoning. NicheStack is used in Operational Technology (OT) devices commonly found in several critical […]
Read More -
Thousands of companies compromised by REvil Ransomware – the supply chain strikes again
On July 2, news emerged of a large-scale attack leveraging the Kaseya VSA network monitoring and management solution to deploy a variant of the REvil ransomware. The attackers claimed that more than a million devices had been infected and they demanded $70 million in Bitcoin to publish a tool to decrypt the files of all […]
Read More -

PrintNightmare
The Infamous Windows Print Spooler Service Hit Again During June’s 2021 Patch Tuesday, Microsoft addressed a minor local privilege escalation (LPE) vulnerability (CVE-2021-1675) in the Windows Print Spooler service (spoolsv.exe), which is responsible for printing management in Windows. Almost two weeks later, the vulnerability impact was changed from LPE to Remote Code Execution (RCE) after […]
Read More -
Our Commitment to Investing in Channel Partners in 2021
The Enterprise of Things has reached a critical mass and companies everywhere across every industry from healthcare to financial services and manufacturing are struggling to defend their networks against unagentable and unmanaged devices, including IoT and OT. Forescout solves this problem today and helps customers secure the hundreds or thousands of devices connecting across their […]
Read More -
When A Critical Vulnerability Meets A Critical Asset
The analysis behind VMware vCenter Server RCE vulnerability On June 4, 2021, the Cybersecurity & Infrastructure Security Agency (CISA) released an alert, asking VMware customers to urgently patch their systems due to the likelihood of cyber threat actors attempting to exploit the company’s vCenter Server and Cloud Foundation products. The related vulnerabilities were assigned respectively […]
Read More -

Addressing TSA’s Security Directive for Pipeline Owners/Operators
Update: On July 19, the Transportation Security Administration (TSA) released their second security directive for pipelines (SD-2021-02), contents of which were made public by the Washington Post on October 3. While the first security directive focused on establishing key roles (e.g. cybersecurity coordinator), definitions, and responsibilities, the second security directive requires adherence to security controls […]
Read More