Post-Quantum Cryptography Risk
Know where to find quantum encryption risk and why it matters now
The risk from quantum computing decryption isn’t evenly distributed, and it isn’t a distant problem. It’s concentrated in specific algorithms, specific communications, and specific data paths. Attackers are already targeting them.
Forescout helps you identify which encrypted traffic is most likely to be harvested today, understand how exposed it is, and reduce that exposure before quantum decryption is viable.
Forescout's Approach

Discover
devices using NON-Quantum safe communications
Patent: US12010210B1

Enforce
network segmentation policy to ensure devices only communicate to trusted systems
Identify & Mitigate
any rogue actors or insecure ports on trusted networks
Create
workflows to identify critical assets PQC capable and orchestrate remediation
Business Outcomes

Identify where exposure exists
Locate encrypted communications that align with high-value target conditions based on their behavior and location.

Understand impact at the asset level
Associate cryptographic weakness with asset importance, data sensitivity, and external access.

Focus on the highest-risk communications
Direct effort toward systems and traffic that contribute the most to potential data exposure.

Reduce what can be harvested over time
Measure how changes in controls and configuration decrease the amount of vulnerable traffic available for collection.
PQC Readiness:
The Next Evolution in Cryptographic Risk Management
PQC readiness involves reducing exposure before migration is complete. Encryption protects data in motion across systems, applications, and networks. The risk depends on where that data flows, how long it remains valuable, and who can access it. Organizations that manage exposure early can limit the amount of sensitive data that may be captured. This approach supports a more controlled transition to quantum-safe cryptography. See the Data
90%
of systems are still not quantum-safe
28%
use PQC-capable OpenSSH for IoT, 16% for OT, and 6% for IoMT devices, revealing a widening readiness gap across device types
2/3
of OT devices in enterprise networks are both high risk and are not PQC-capable on TLS
How Forescout Powers PQC Readiness
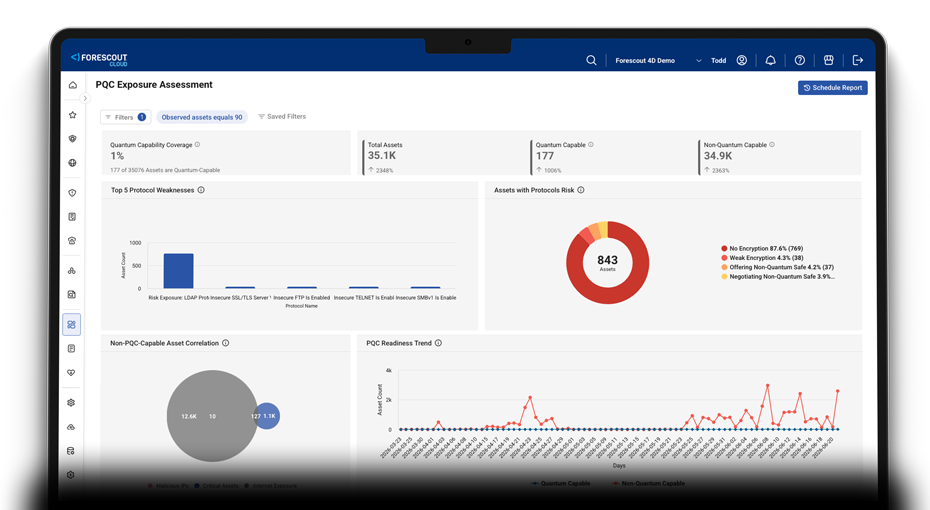
Forescout powers PQC readiness by transforming fragmented cryptographic data into a unified, real-time view of quantum risk across IT, OT, and IoT environments. It evaluates encryption within the context of real network behavior, builds a complete cryptographic inventory, and applies context to identify the most critical exposures. By enabling prioritization, policy enforcement, and remediation workflows, Forescout helps organizations reduce risk today while guiding a structured transition to quantum-safe security.
Your journey to PQC readiness starts with the Forescout Vistaro™ platform: the only platform with patented PQC technology and agentic AI.
- Observe encryption across active communications
Understand how systems interact and where vulnerable cryptography is in use - Identify communications with higher exposure characteristics
Highlight traffic involving sensitive data, external connectivity, or persistent value - Assess impact based on real conditions
Connect cryptographic use to asset role, location, and accessibility - Apply controls to reduce exposure
Limit access paths, segment traffic, and reduce the amount of data that can be collected
Frequently Asked Questions
Can Forescout detect whether my encryption is quantum-safe?
Yes. Forescout developed and patented technology that detects and inventories quantum-safe and non-quantum-safe encryption usage in real time, without agents – Forescout’s Quantum-Safe Security Assurance. Invented in 2023 and patented in 2024, it continuously analyzes device encryption to pinpoint post-quantum vulnerabilities across IT, OT and IoT, with dedicated PQC dashboards.
Can Forescout show whether my encryption is protected from quantum computing?
Yes. Forescout’s Quantum-Safe Security Assurance identifies, assesses and closes post-quantum cryptography gaps across IT, OT and IoT by continuously analyzing device encryption without agents, and Forescout’s PQC dashboards quantify quantum exposure by environment.
Can Forescout automatically see if my SSH is safe from quantum decryption?
Yes. Forescout’s patented technology continuously analyzes device encryption without agents to detect and inventory quantum-safe and non-quantum-safe usage.
What are the quantum capabilities of Forescout’s PQC solution?
Forescout’s PQC capabilities are a risk driven, behavior based quantum security assurance solution that delivers real-time visibility, contextual risk analysis, and prioritization of cryptographic risk across an organization’s environment.
It moves beyond static discovery by enabling organizations to continuously see, understand, prioritize, and act on post quantum cryptography (PQC) risk in live environments.
How is this different from traditional cryptographic discovery tools?
Traditional tools focus on point‑in‑time scans or static inventories. Forescout’s PQC capabilities is different because it:
- Provides continuous, real-time discovery of cryptographic usage
- Ties findings to actual behavior and exposure
- Enables risk prioritization based on context
- Supports a path toward mitigation and control, not just visibility
Does the Forescout PQC solution provide a cryptographic inventory?
Yes. The platform builds a network-wide cryptographic inventory, including:
- Cipher usage across assets
- Associations with asset context
- Inputs for prioritization and future remediation
How does the Forescout PQC solution prioritize risk?
Risk is prioritized using real-world context, such as:
- External vs internal communications
- Protocol sensitivity
- Exposure to malicious or high-risk destinations
- Asset criticality and data sensitivity
This ensures you can focus on what matters first, not just what exists.