Forescout Research –
Vedere Labs
“Vedere” is the Italian word meaning “to see,” which epitomizes the mission of Forescout Vedere Labs, the cybersecurity research arm of Forescout. Our team of global experts focuses on increasing visibility of cybersecurity threats and vulnerabilities for all connected asset types and providing mitigation steps organizations can use to protect themselves.
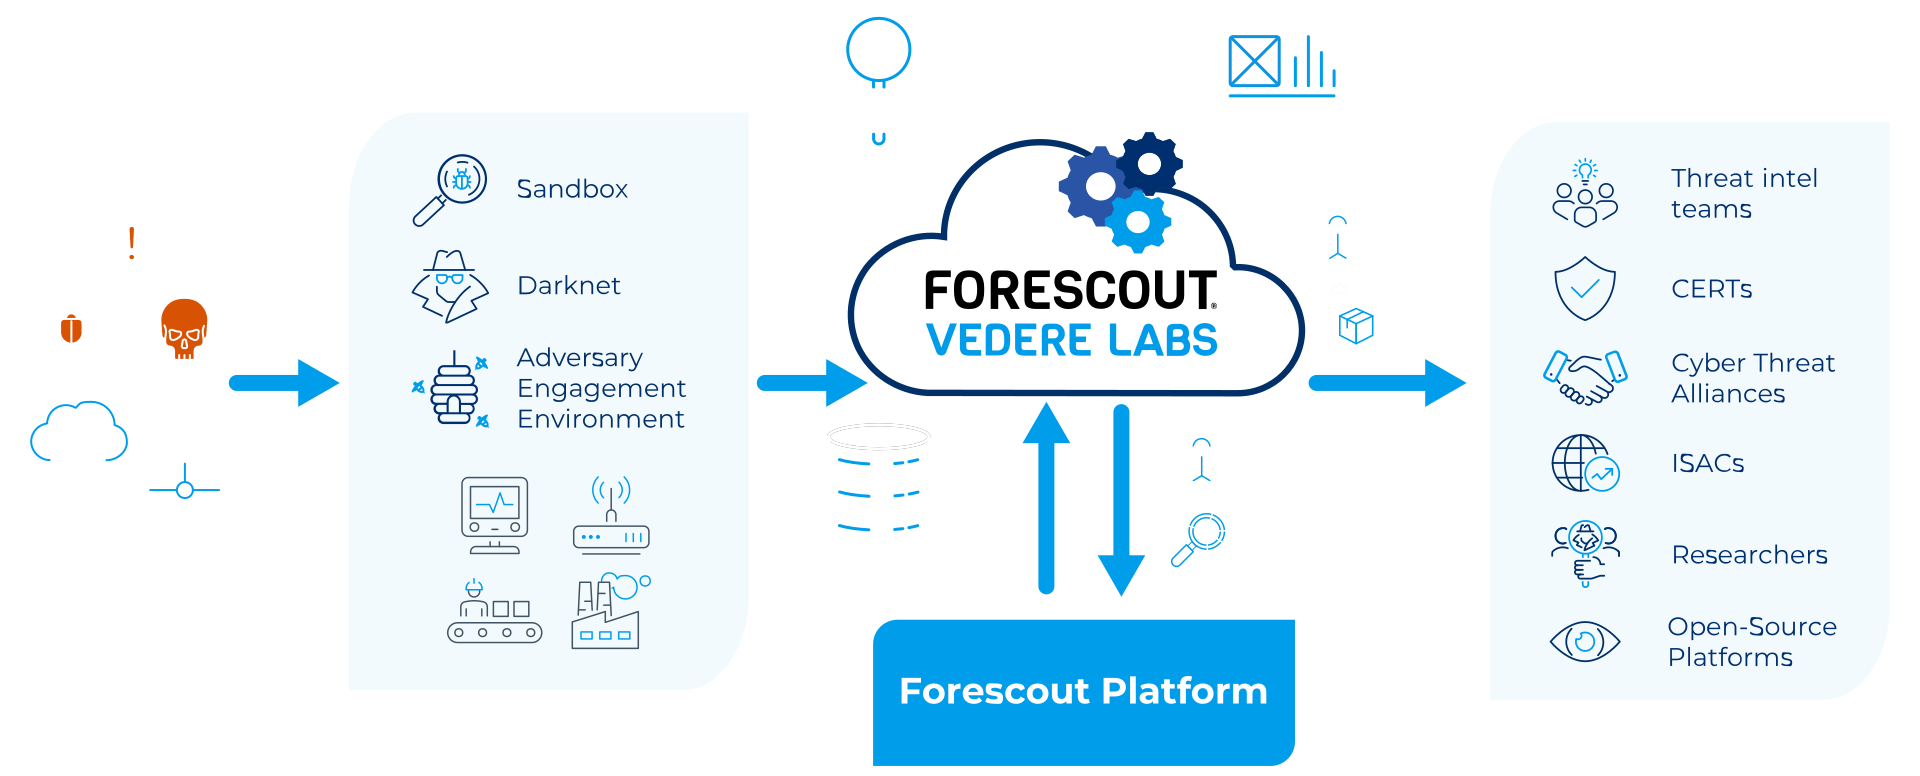
Our research is fed into the Forescout Platform and shared with the cybersecurity community, including CISA and other cybersecurity agencies, CERTs, ISACs, open-source projects, device manufacturers, universities and other researchers.
What We Do
Vulnerability Research
- Focus on vulnerabilities against managed and unmanaged devices (IT/IoT/IoMT/OT)
- 200+ vulnerabilities discovered in last 5 years
- 100+ known exploited vulnerabilities on unmanaged devices
Threat Reports
- Manual and automatic analysis of malware samples collected via customer telemetry and other sources
Threat Intelligence & Detection
- Daily context-rich, machine-consumable threat feeds
- Detection rules to keep our Threat Detection & Response solution on top of emerging threats
- Live dashboards
How We Do It
Forescout Vedere Labs studies what attackers are working towards by observing actual attacks in our sandboxes, on the Darknet and in our Adversary Engagement Environment. We analyze significant attacks and generate vulnerability and threat intelligence that is consumed by the Forescout Platform. We also create corresponding detection rules that are added to Forescout Threat Detection & Response to help ensure customers can protect their IT, OT, IoT and IoMT environments.
Firsthand Observations in Our Research Laboratory
Located in Eindhoven, Netherlands, our research laboratory is where we observe firsthand the vulnerabilities being exploited and attacks in progress. The information we collect is analyzed to generate threat intelligence, calculate multifactor risk scores and create detection rules.
How Vedere Labs Uses Artificial Intelligence
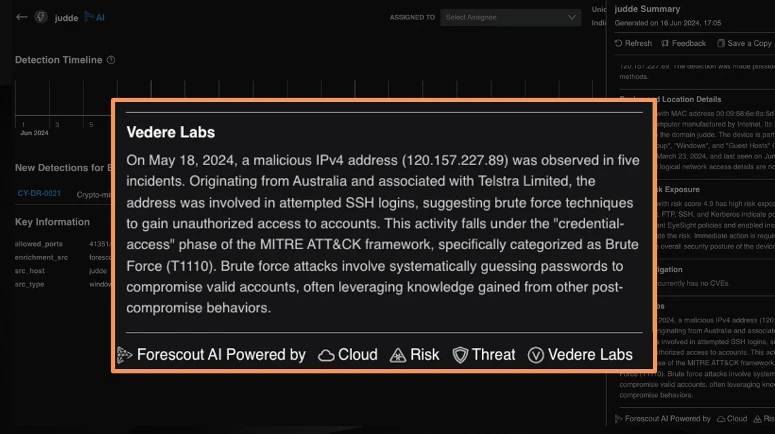
VL threat intelligence is integrated on generative AI products, such as Microsoft Copilot for Security, allowing security analysts to query OT and IoT-specific threat intelligence directly from Forescout Research.
We also have integrated generative AI within our TDR solution, which summarizes proprietary intelligence that can be gathered about IP addresses and other indicators of compromises observed during an incident.
VL KEV: Our Proprietary List of Vulnerabilities
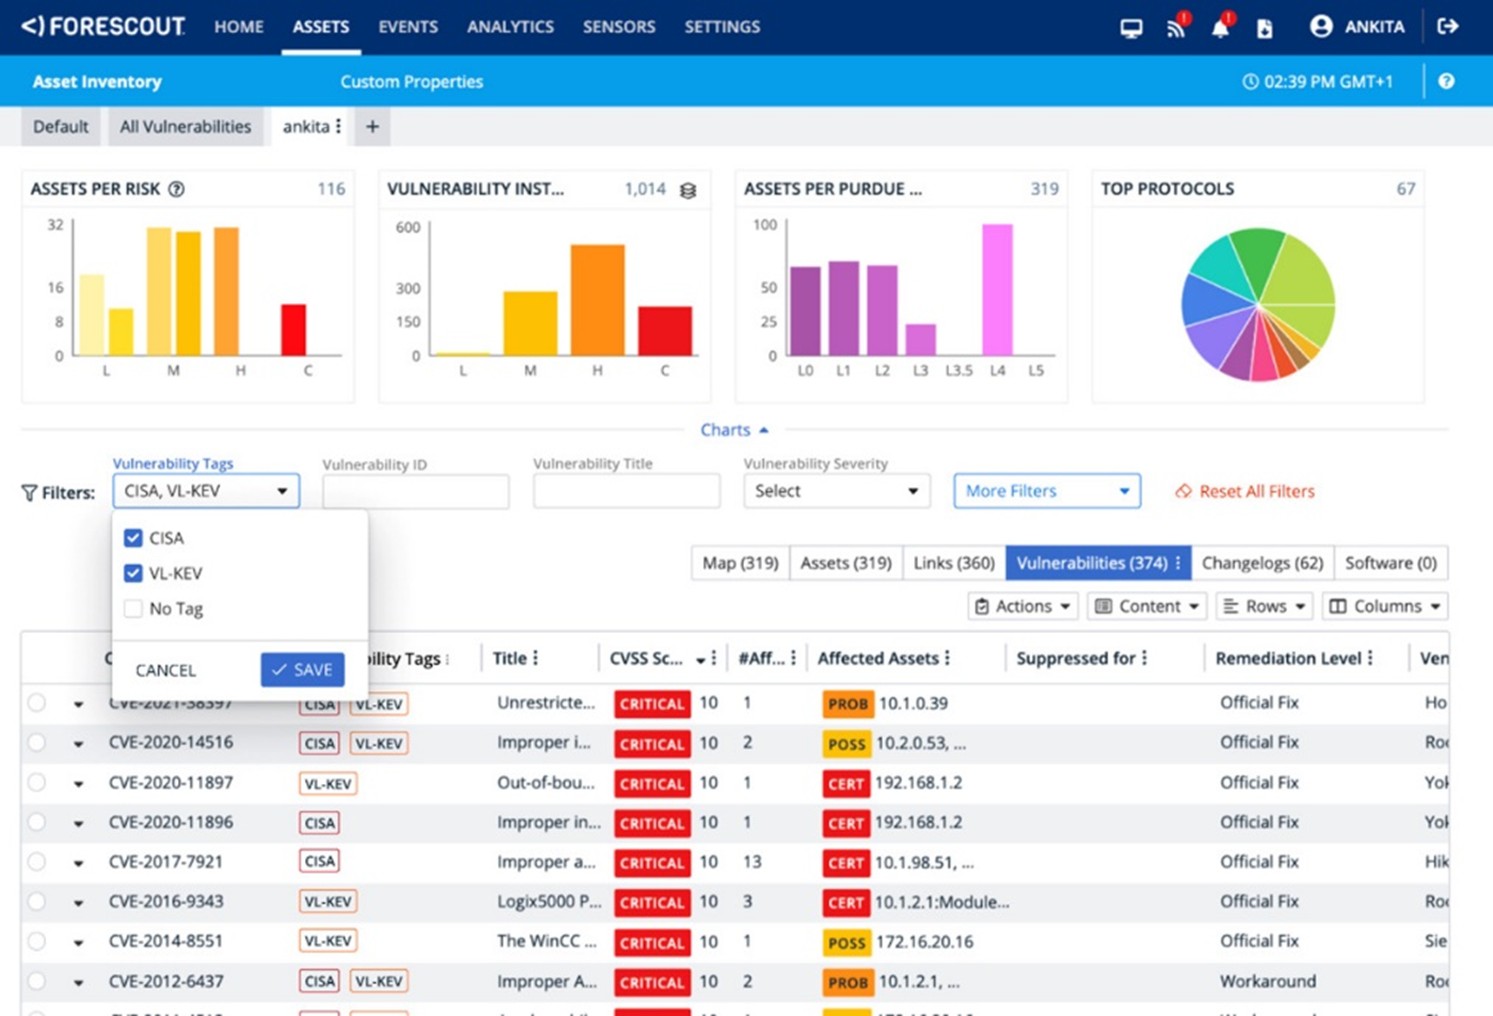
Our KEV list is compiled from real attacks we observe within our OT and IoT-specific honeypots, customer data and third-party intelligence. The list is complementary to industry-standard sources, such as CISA KEV. It is updated in tandem with other threat intelligence for Forescout eyeInspect and REM solutions. This type of intelligence allows users to prioritize vulnerability management actions based on what is currently being exploited by threat actors.
Partnerships and Threat Intelligence Sharing Groups
Vedere Labs is a proud member and contributor to threat intelligence sharing groups, including CERTs, cyber threat alliances and ISACs — where new intelligence and best practices are shared. Member organizations include industry, academia and governments where we share machine-readable intelligence and human-readable reports.
European Energy ISAC
Forescout is a founding member and actively participates in the threat intelligence task force.
ETHOS
Forescout is a founding member and part of the board of directors in this industry partnership dedicated to OT-centric, open-source sharing of anonymous early-warning threat information.
OT-ISAC
Forescout is a partner that shares reports, answers questions about emerging threats and presents at conferences and threat briefing meetings.
CISA JCDC and AIS
Forescout shares indicators of compromise and reports distributed to other members of the JCDC and IAS initiatives.
ACSC CTIS
Forescout shares indicators of compromise and reports distributed to other members of the CTIS initiative.
Data. Lots of Data.
The threat intelligence data we analyze comes from millions of connected devices that we monitor that give us billions of data points about device configuration and network behavior. It also comes from attacks we observe and dissect and other sources that we monitor.
Devices
- 19 million monitored devices
- 39 billion unique data points
- 1,500 global sites
- 6,500+ unique vendors
- 2,300+ unique OS versions
Threats
- 750+ threat actors
- 100+ ransomware group leak sites
- 20+ C2 types monitored on the Internet
- Third-party intel
Forescout Research - Vedere Labs Featured In...
Researchers uncover software flaws leaving medical devices vulnerable to hackers
Researchers say they have found more than a dozen vulnerabilities in software used in medical devices and machinery used in other industries that, if exploited by a hacker, could cause critical equipment such as patient monitors to crash…
Read More
Critical Bugs Expose Hundreds of Thousands of Medical Devices and ATMs
“You can imagine the type of impact an attacker could have when they can either exfiltrate data from medical equipment or other sensitive devices, potentially tamper with lab results, make critical devices unavailable, or take them over entirely…”
Read More
Government cyber workers increasingly concerned hackers will strike during shutdown
The government’s cybersecurity professionals are increasingly concerned that hackers will take advantage of the partial shutdown to tamper with sensitive government data or steal citizens’ information — and that the bare-bones staff won’t be able to fend them off…
Learn More
OT:ICEFALL FINALE
Forescout Vedere Labs is wrapping up its yearlong project looking at design vulnerabilities in operational technology with a closing report today that blames many of the issues they’ve encountered on vendors of the technology not implementing designs that would build security into the systems…
Read More
Dray:Break
In 2024, routers are a primary target for cybercriminals and state-sponsored attackers – and are the riskiest device category on networks. We investigated one hardware vendor, DrayTek, with a history of security flaws to help it address its issues and prevent new attacks — especially when ransomware and denial of service attacks are so high today.
Forescout Research. In Your Inbox. Every Month
With 13 cyber attacks every second, it’s hard to keep up.
To help, Vedere Labs now has its own newsletter. Curated by our research leaders, you’ll receive the most crucial information you need to stay ahead of attackers.
It’s loaded with useful context, links and spotlights on threat actors, newly exploited vulnerabilities and other must-know asset intelligence. Once a month. Nice and easy.
Meet Our Leader
Daniel dos Santos
Daniel dos Santos is the Head of Research at Forescout Vedere Labs, where he leads a team of researchers that identifies new vulnerabilities and monitors active threats. He holds a PhD in computer science, has published over 35 peer-reviewed papers, has found or disclosed hundreds of CVEs — and is a frequent speaker at security conferences.
Explore Vedere Labs Blogs
-
How Do You Know If You’re Covered for TTPs in CISA Critical Advisories?
Depending on what the world’s threat actors are up to and whether their activity is detected, CISA may issue a cybersecurity advisory (CSA) every few days or have nothing for a month. It’s hard to predict, and you never know what’s coming your way. One thing is certain: If you managed cybersecurity for a critical […]
Read More -
Mass Exploitation of MOVEit Transfer Critical Vulnerability – Recommended Mitigations and How Forescout Can Help
On May 31, Forescout Research – Vedere Labs uncovered a significant incident where threat actors exploited a critical zero-day vulnerability in the MOVEit Transfer software, which resulted in unauthorized access to and exfiltration of private data, as well as privilege escalation. MOVEit Transfer is a widely adopted managed file transfer (MFT) solution that enables organizations […]
Read More -
AI-Assisted Attacks Are Coming to OT and Unmanaged Devices – the Time to Prepare Is Now
Malicious code is not difficult to find these days, even for OT, IoT and other embedded and unmanaged devices. Public exploit proofs-of-concept (PoCs) for IP camera vulnerabilities are routinely used by Chinese APTs, popular building automation devices are targeted by hacktivists and unpatched routers used for Russian espionage. Threat actors typically port these PoCs into […]
Read More -
Three New BGP Message Parsing Vulnerabilities Disclosed in FRRouting Software
In our new vulnerability research report, Forescout Vedere Labs discusses an often-overlooked aspect of Border Gateway Protocol (BGP) security: vulnerabilities in its software implementations. More specifically, vulnerabilities in BGP message parsing found in the popular FRRouting implementation that could be exploited by attackers to achieve a denial of service (DoS) condition on vulnerable BGP peers. […]
Read More -
How to Detect and Mitigate the 3CXDesktopApp Supply Chain Attack
On March 29, researchers from two security companies identified an active campaign originating from a modified version of a legitimate, signed application: 3CXDesktopApp, a popular voice and video conferencing software. 3CXDesktopApp is developed by 3CX, a business communications software company. According to its website, 3CX has 600,000 client organizations and 12 million daily users. 3CX […]
Read More -
Forescout Research – Vedere Labs Releases String Deobfuscation Tool for Analysis of Mirai IoT Botnet Variants
As part of our recently released 2022 Threat Roundup report, Forescout Vedere Labs described how the Mirai IoT botnet continues to evolve via new variants and adaptations, such as Gafgyt and RapperBot, more than six years after it started taking over IoT devices and had its source code leaked. Extracting strings from these Mirai variants […]
Read More -
2022 Threat Roundup: The Emergence of Mixed IT/IoT Threats
Rapid digitization means that organizations are now more connected than ever. Most organizations now host a combination of interconnected IT, OT, IoT and sometimes IoMT devices in their networks, which has increased their attack surface. Forescout’s data shows that around 24% of connected devices in every organization are no longer traditional IT. The growing number […]
Read More -
Asset Visibility and Behavior: The Keys to Segmentation Success
Recently, Gartner® refreshed one of its foundational cybersecurity research, “The 6 Principles of Successful Network Segmentation Strategies.”1 The principles covered in the research are tried and true. Segmenting networks to improve security and performance is nothing new to security teams, yet the same challenges persist year after year. Gartner analysts are keenly aware of that, having […]
Read More -
Introducing Forescout XDR: Putting the X, D and R Back in XDR
According to a Mandiant survey of 1,350 global business and IT leaders, when trying to secure their networks against cyber threats, nearly all respondents (96%) believe it’s important to understand the threat actors targeting their organizations. That’s hardly a surprise. But then there’s this finding: 79% of respondents say that most of the time, they […]
Read More