Forescout Research –
Vedere Labs
“Vedere” is the Italian word meaning “to see,” which epitomizes the mission of Forescout Vedere Labs, the cybersecurity research arm of Forescout. Our team of global experts focuses on increasing visibility of cybersecurity threats and vulnerabilities for all connected asset types and providing mitigation steps organizations can use to protect themselves.
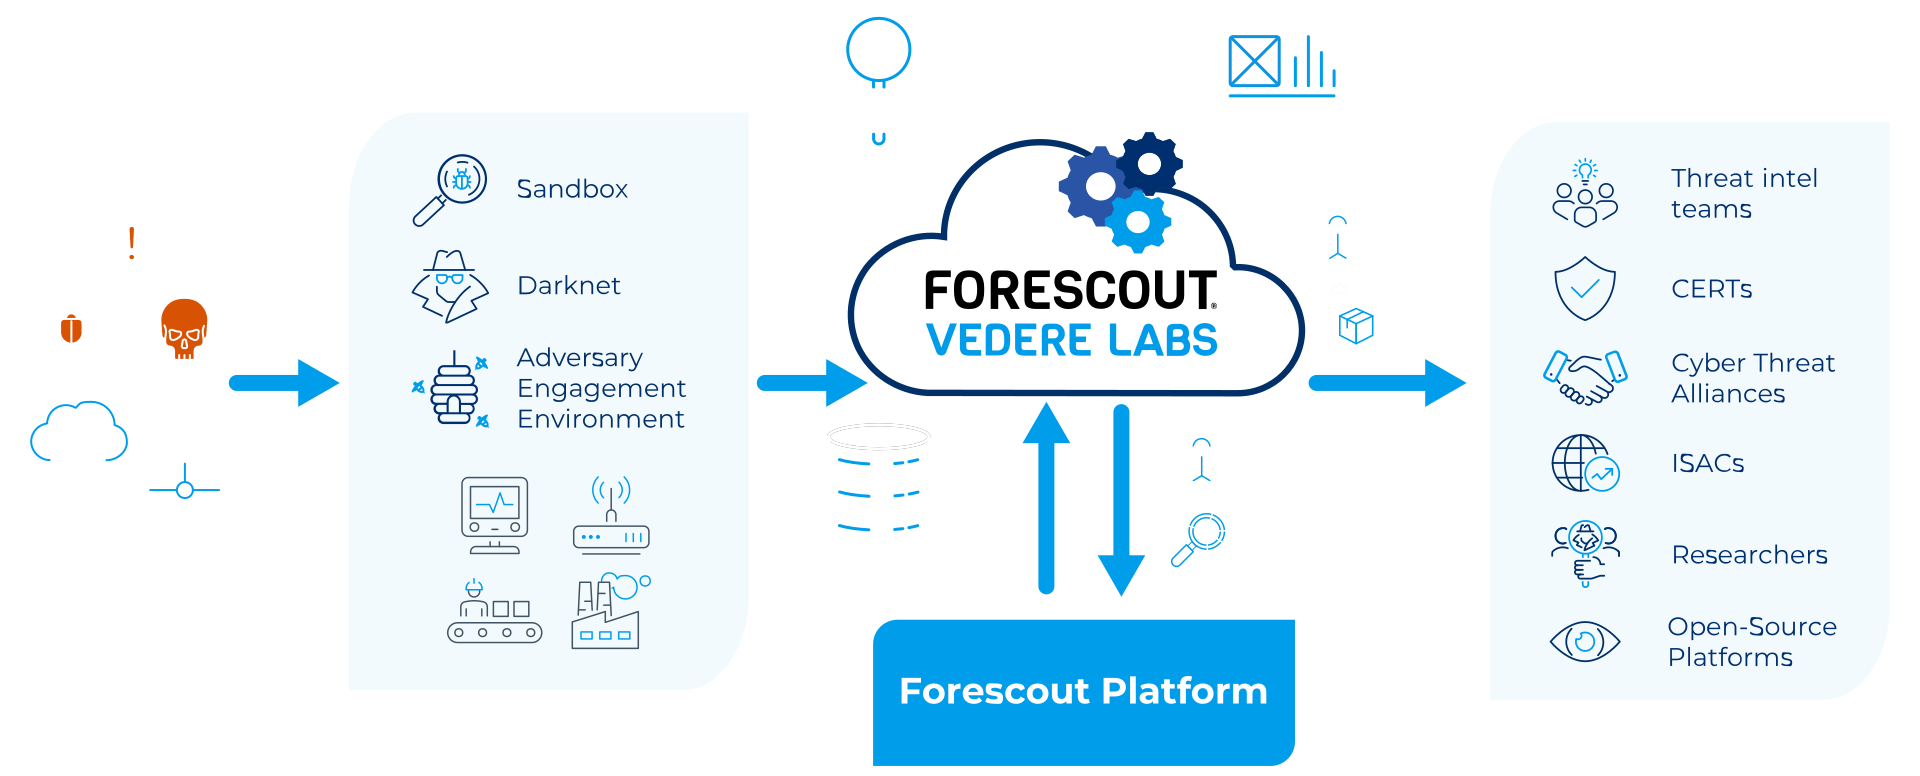
Our research is fed into the Forescout Platform and shared with the cybersecurity community, including CISA and other cybersecurity agencies, CERTs, ISACs, open-source projects, device manufacturers, universities and other researchers.
What We Do
Vulnerability Research
- Focus on vulnerabilities against managed and unmanaged devices (IT/IoT/IoMT/OT)
- 200+ vulnerabilities discovered in last 5 years
- 100+ known exploited vulnerabilities on unmanaged devices
Threat Reports
- Manual and automatic analysis of malware samples collected via customer telemetry and other sources
Threat Intelligence & Detection
- Daily context-rich, machine-consumable threat feeds
- Detection rules to keep our Threat Detection & Response solution on top of emerging threats
- Live dashboards
How We Do It
Forescout Vedere Labs studies what attackers are working towards by observing actual attacks in our sandboxes, on the Darknet and in our Adversary Engagement Environment. We analyze significant attacks and generate vulnerability and threat intelligence that is consumed by the Forescout Platform. We also create corresponding detection rules that are added to Forescout Threat Detection & Response to help ensure customers can protect their IT, OT, IoT and IoMT environments.
Firsthand Observations in Our Research Laboratory
Located in Eindhoven, Netherlands, our research laboratory is where we observe firsthand the vulnerabilities being exploited and attacks in progress. The information we collect is analyzed to generate threat intelligence, calculate multifactor risk scores and create detection rules.
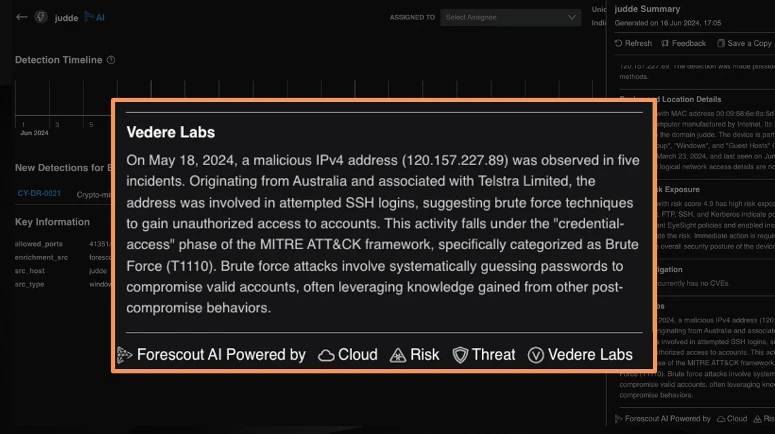
How Vedere Labs Uses Artificial Intelligence
VL threat intelligence is integrated on generative AI products, such as Microsoft Copilot for Security, allowing security analysts to query OT and IoT-specific threat intelligence directly from Forescout Research.
We also have integrated generative AI within our TDR solution, which summarizes proprietary intelligence that can be gathered about IP addresses and other indicators of compromises observed during an incident.
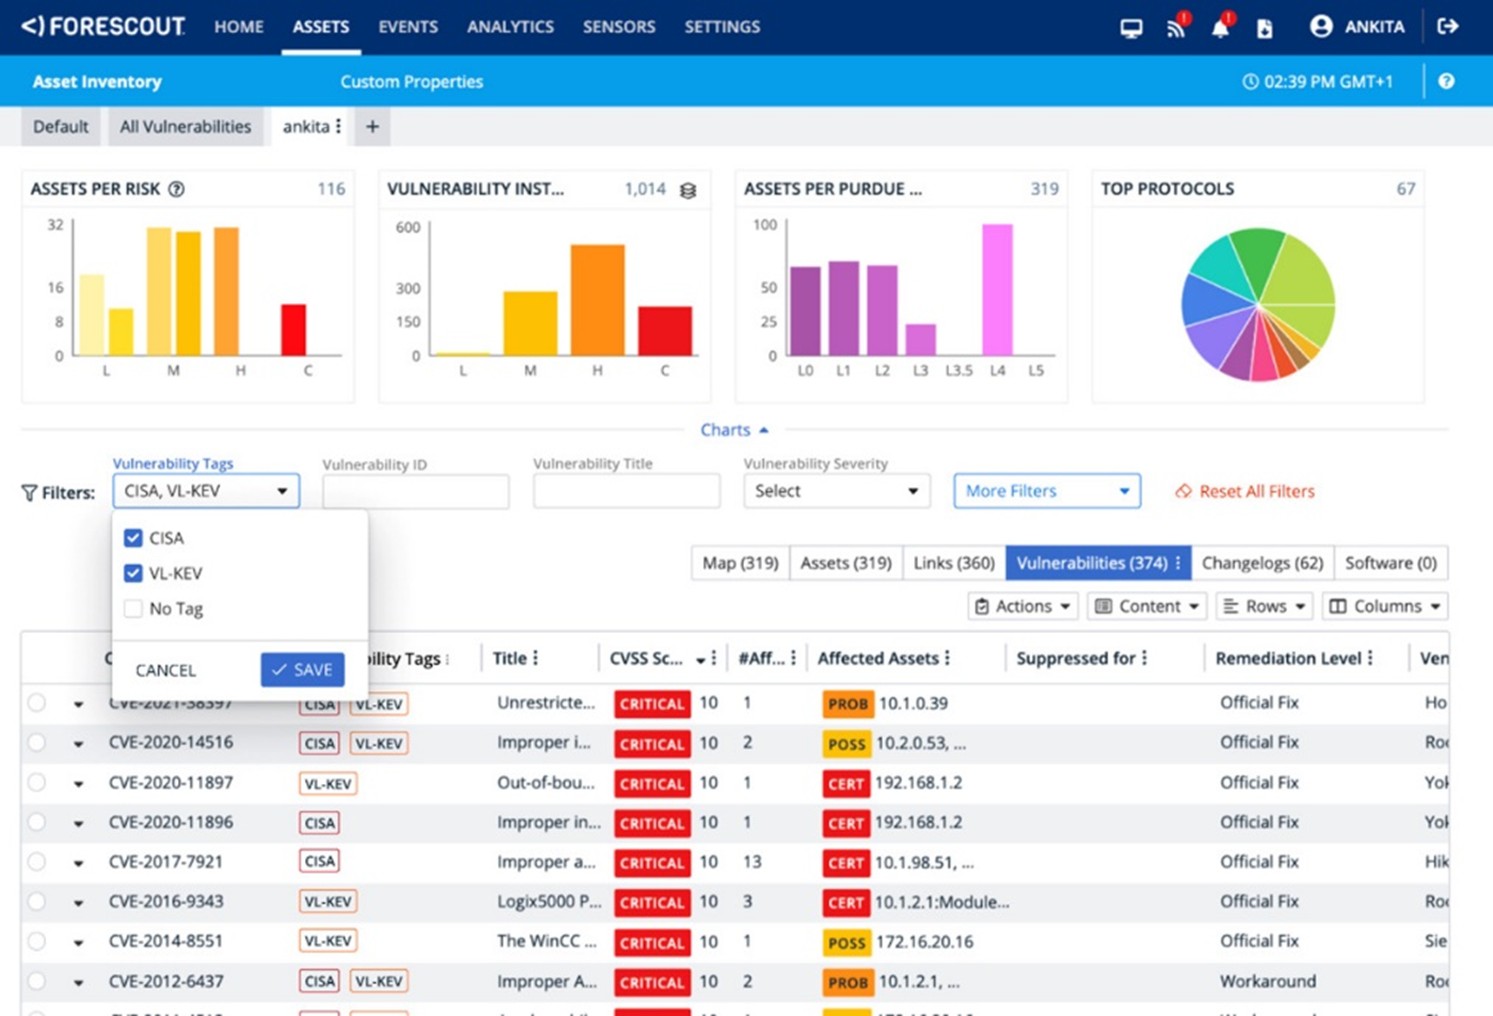
VL KEV: Our Proprietary List of Vulnerabilities
Our KEV list is compiled from real attacks we observe within our OT and IoT-specific honeypots, customer data and third-party intelligence. The list is complementary to industry-standard sources, such as CISA KEV. It is updated in tandem with other threat intelligence for Forescout eyeInspect and REM solutions. This type of intelligence allows users to prioritize vulnerability management actions based on what is currently being exploited by threat actors.
Partnerships and Threat Intelligence Sharing Groups
Vedere Labs is a proud member and contributor to threat intelligence sharing groups, including CERTs, cyber threat alliances and ISACs — where new intelligence and best practices are shared. Member organizations include industry, academia and governments where we share machine-readable intelligence and human-readable reports.
European Energy ISAC
Forescout is a founding member and actively participates in the threat intelligence task force.
ETHOS
Forescout is a founding member and part of the board of directors in this industry partnership dedicated to OT-centric, open-source sharing of anonymous early-warning threat information.
OT-ISAC
Forescout is a partner that shares reports, answers questions about emerging threats and presents at conferences and threat briefing meetings.
CISA JCDC and AIS
Forescout shares indicators of compromise and reports distributed to other members of the JCDC and IAS initiatives.
ACSC CTIS
Forescout shares indicators of compromise and reports distributed to other members of the CTIS initiative.
Data. Lots of Data.
The threat intelligence data we analyze comes from millions of connected devices that we monitor that give us billions of data points about device configuration and network behavior. It also comes from attacks we observe and dissect and other sources that we monitor.
Devices
- 19 million monitored devices
- 39 billion unique data points
- 1,500 global sites
- 6,500+ unique vendors
- 2,300+ unique OS versions
Threats
- 750+ threat actors
- 100+ ransomware group leak sites
- 20+ C2 types monitored on the Internet
- Third-party intel
Forescout Research - Vedere Labs Featured In...
Researchers uncover software flaws leaving medical devices vulnerable to hackers
Researchers say they have found more than a dozen vulnerabilities in software used in medical devices and machinery used in other industries that, if exploited by a hacker, could cause critical equipment such as patient monitors to crash…
Read More
Critical Bugs Expose Hundreds of Thousands of Medical Devices and ATMs
“You can imagine the type of impact an attacker could have when they can either exfiltrate data from medical equipment or other sensitive devices, potentially tamper with lab results, make critical devices unavailable, or take them over entirely…”
Read More
Government cyber workers increasingly concerned hackers will strike during shutdown
The government’s cybersecurity professionals are increasingly concerned that hackers will take advantage of the partial shutdown to tamper with sensitive government data or steal citizens’ information — and that the bare-bones staff won’t be able to fend them off…
Learn More
OT:ICEFALL FINALE
Forescout Vedere Labs is wrapping up its yearlong project looking at design vulnerabilities in operational technology with a closing report today that blames many of the issues they’ve encountered on vendors of the technology not implementing designs that would build security into the systems…
Read More
Dray:Break
In 2024, routers are a primary target for cybercriminals and state-sponsored attackers – and are the riskiest device category on networks. We investigated one hardware vendor, DrayTek, with a history of security flaws to help it address its issues and prevent new attacks — especially when ransomware and denial of service attacks are so high today.
Forescout Research. In Your Inbox. Every Month
With 13 cyber attacks every second, it’s hard to keep up.
To help, Vedere Labs now has its own newsletter. Curated by our research leaders, you’ll receive the most crucial information you need to stay ahead of attackers.
It’s loaded with useful context, links and spotlights on threat actors, newly exploited vulnerabilities and other must-know asset intelligence. Once a month. Nice and easy.
Meet Our Leader
Daniel dos Santos
Daniel dos Santos is the Head of Research at Forescout Vedere Labs, where he leads a team of researchers that identifies new vulnerabilities and monitors active threats. He holds a PhD in computer science, has published over 35 peer-reviewed papers, has found or disclosed hundreds of CVEs — and is a frequent speaker at security conferences.
Explore Vedere Labs Blogs
-
Forescout Cyber Weekly Roundup <br>September 13, 2019
Public Sector A brave new, 5G world for Chinese cybersecurity: The roll-out of 5G—the “connective tissue” for the IoT, smart cities, revolutionary healthcare and driverless cars—will open up more opportunities for cybersecurity companies, the chairman and CEO of Chinese internet security provider Qihoo 360, Zhou Hongyi, said in a recent interview. As advanced technology gets […]
Read More -
Accelerating Development of Future Cloud Offerings
It is always exciting to take a leap forward in delivering upon a vision. For Forescout, our vision is to help customers solve one of the biggest problems in cyber today – enabling a secure enterprise amidst the explosion of managed and unmanaged devices quickly infiltrating corporate networks. It is an important and growing problem. […]
Read More -
The Rise of Botnets
Twitter: @MeetCyberBob There is a new variety of the Mirai Botnet on the rise. This time, instead of largely attacking IP cameras, it includes TVs and other network-centric devices. The attacks are evolving to include more enterprise-class systems as well, making risk assessment in businesses much more difficult. We are all consumers of these technologies. The attack […]
Read More -
Forescout Recognized by Frost & Sullivan for Achievements in Smart Building Cybersecurity
Frost & Sullivan, a global leader in market research and business analysis, has recognized Forescout for its IT-OT cybersecurity advancements and achievements for smart buildings with the 2019 Global Enabling Technology Leadership Award. This accolade is awarded to companies who have both superior technologies that are flexible and innovative, and who also demonstrate high levels […]
Read More -
Minimizing Cybersecurity Impact from Human Error in ICS Networks
Most industry professionals agree that malicious activities from outside of an organization are a huge risk, so they prioritize strengthening external protections and keep a constant watch on their surroundings. What might come as a surprise is that, last year, 52% of security incidents affecting industrial control systems (ICS) and operational technology (OT) networks were […]
Read More -
How to Stay Protected Against BlueKeep and DejaBlue?
BlueKeep is still one of the most daunting threats to our systems out there. The vulnerability is still a potential security challenge despite multiple patches released by Microsoft and third parties. Additionally, while fixing the BlueKeep flaw, Microsoft discovered other vulnerabilities, dubbed “DejaBlue”. With the device explosion of IT and OT convergence, and the Internet […]
Read More -
Forescout Cyber Weekly Roundup <br>September 5, 2019
The Forescout Cyber Roundup is a weekly blog series that highlights some of the major cyber headlines, as well as some of the more obscure stories from the week. The purpose of this curation is to raise cyber awareness, provoke thought and encourage discussion among cyber professionals at all levels. Articles are categorized by industry, […]
Read More -
Do you know every device connected to your enterprise? If so, congrats—94% of businesses don’t!
Twitter: @MeetCyberBob SANS’ distinguished analyst Don Murdoch recently did a thorough review of my company’s network device visibility and control platform. The review, titled Device Visibility and Control: Streamlining IT and OT Security with Forescout, evaluated the latest product version, Forescout 8.1, which incorporates our acquisition of SecurityMatters’ device visibility technology from the OT world […]
Read More -
Device Visibility and Control: A SANS Perspective on Forescout 8.1
As digital transformation continues, organizations are rethinking their security strategies, with a renewed focus on complete visibility into every device connecting to extended enterprise networks. This first step toward understanding and mitigating risk, visibility is also the foundation for safety, availability and uptime in operational (OT) networks. Add to that new Internet of Things (IoT) […]
Read More