CYBERSECURITY A-Z
Secure remote access (SRA) is the combination of technologies, policies, and security controls that let authorized users and devices connect safely to an organization’s network, applications, and resources from outside the corporate office while preventing unauthorized access. It verifies identity, encrypts data in transit, and continuously enforces least-privilege access so that remote and hybrid work never become open doors for attackers.
SRA covers every scenario in which someone outside the physical network needs to reach internal systems, such as remote and hybrid employees, third-party vendors, contractors, and field engineers maintaining equipment. Rather than simply opening a connection, it applies authentication, encryption, and policy-based controls to ensure that only the right people reach only the resources they need, and that sensitive data stays protected the entire time. Effective secure remote access spans both managed corporate devices and the unmanaged, third-party, and operational-technology endpoints that traditional tools often miss, giving security teams a single, consistent way to govern every remote connection.
How Secure Remote Access Differs From Basic Remote Access
Basic remote connectivity – a traditional VPN tunnel or an exposed remote-desktop gateway – grants broad, trusted network access the moment a user connects. By contrast, secure remote access verifies identity before granting entry, scopes each session to specific systems using least privilege, encrypts the traffic, and monitors activity throughout. In other words, a connection no longer equals unlimited trust.
Secure Remote Access Also Applies to CPS/OT Environments
Gartner defines SRA in cyber-physical systems (CPS) and operational technology (OT) as: “products that enable employees, contractors or original equipment manufacturers (OEMs) to safely and securely operate, maintain or update CPS remotely. These products provide a robust mechanism to verify remote users’ authenticity and authorization, enforce granular access policies for both users and systems, ensure secure communications, and track the integrity of user actions. Organizations can deploy these products in cloud, on-premises or in a hybrid environment.”
The problem is remote access was never intended in most legacy CPS and OT systems. Many of these systems lack the native identity, authentication, and authorization controls required for safe remote operations. Forescout explored some of this insecure-by-design functionality in operational technology (OT) in OT:ICEFALL research from Vedere Labs.
Remote access is also one of the least governed paths into CPS environments because of the continued use of VPNs and jump hosts. Once connected through these methods, users often gain broad, persistent access.
How Does SRA Work?
Secure remote access works by layering several controls so that access is earned continuously, not just granted once. Several core mechanisms (listed below) work in unison across the life of every session. The goal is to replace the old model of ‘authenticate once, then trust broadly’ with a new model where trust is narrow, explicit, and constantly re-checked.
Strong Authentication and Authorization
Before any access is granted, the user’s identity is verified — typically through single sign-on (SSO) and multi-factor authentication — and an authorization check confirms exactly which systems that identity is allowed to reach.
Granular, Role-Based Access Policies
Access is scoped to the specific applications and systems which a role requires, following the principle of least privilege, so a single remote session can never reach the entire network.
Encryption of Data in Transit
Encrypted tunnels and end-to-end encryption protect data as it moves between the remote device and corporate resources, helping maintain a secure connection and keep data confidential even over untrusted networks.
Device Posture Checks and Continuous Verification
The connecting device is checked for patch level and security posture before access, and — following zero-trust principles — the session is continuously re-verified rather than trusted indefinitely once connected.
Endpoint and Session Monitoring
Active sessions are monitored for anomalous behavior, and malicious or out-of-policy activity can be blocked automatically before it causes harm.
Core Remote Access Technologies
Several technology categories deliver secure remote access, and they often do so in combination. Each solves a different part of the ‘connect-safely’ problem. In practice, most organizations combine several of these as they modernize away from network-centric access in favor of identity- and application-centric models.
Virtual Private Networks (VPN)
A remote access VPN — a virtual private network built for users outside the office — creates an encrypted tunnel across the public internet to the corporate network. Remote access VPN protocols such as IPsec and SSL/TLS carry that tunnel, and remote access VPN client software on the endpoint authenticates the user before any traffic flows. The gateway’s remote access VPN security features then keep unauthorized traffic off the network. VPNs are widely deployed, but they tend to grant broad network access once a user connects, which limits how tightly an individual session can be controlled.
Zero Trust Network Access (ZTNA)
Zero Trust Network Access (ZTNA) verifies identity and device context on every request, then grants access only to the specific, authorized applications a role requires rather than to the whole network. Following zero trust architecture principles, it re-verifies each session continuously and never treats network location as a reason to trust a connection. That is what makes ZTNA a more granular successor to the VPN model.
Secure Access Service Edge (SASE)
SASE converges networking and security into a cloud-delivered service, extending consistent secure-access policy to distributed users and sites without backhauling all traffic through a data center.
Remote Desktop Protocol (RDP), SSH, and VNC
RDP, SSH, and VNC are remote-session protocols used to operate systems from afar. A secure remote access platform brokers and monitors these sessions instead of exposing them directly to the internet, closing one of the most commonly exploited entry points.
VPN vs. ZTNA vs. SASE: Comparing Remote Access Approaches
The three dominant approaches differ mainly in how much they trust the network and how granular their access is. The table below summarizes the trade-offs:
| Approach | Access Model | Best Fit |
|---|---|---|
| VPN | Encrypted tunnel; broad network access once authenticated | Simple, established remote connectivity for trusted employees |
| ZTNA | Identity- and context-verified access to specific apps; continuous verification | Least-privilege access for employees, vendors, and unmanaged devices |
| SASE | Cloud-delivered convergence of networking and security policy | Distributed, cloud-first organizations with many sites and users |
Many organizations run more than one at a time — keeping VPN for legacy needs while moving high-risk or third-party access to ZTNA, and adopting SASE as they consolidate networking and security in the cloud. The practical direction of travel is away from implicit network trust and toward identity-verified, least-privilege access that can be applied uniformly to employees, vendors, and unmanaged assets alike.
Go deeper: See why you need a more universal approach to network access with zero trust in: “A CISO’s Guide to UZTNA”.
Watch Dr. Chase Cunningham (Dr.ZeroTrust) talk about how to truly operationalize Zero Trust
Key Security Measures in Secure Remote Access
A secure remote access deployment relies on a handful of controls working together. None of them is sufficient alone, and when layered together, they minimize the damage from a compromised credential or device.
Multi-Factor Authentication (MFA)
MFA requires two or more verification methods — such as a password plus a mobile token or biometric — before granting access. This sharply reduces the risk from stolen credentials.
End-to-End Encryption
Encryption protects data across the full transmission path so it stays confidential even if intercepted.
Principle of Least Privilege
Users receive access only to the exact systems and files their role requires, which limits the blast radius if an account is ever compromised.
Endpoint Security and Device Compliance
Before they are trusted to connect, devices must meet a security-posture baseline — up-to-date patches, endpoint protection, and compliance checks.
Why Is Secure Remote Access Important?
As remote work and hybrid work, bring-your-own-device (BYOD) policies, and cloud-hosted applications have become standard, the number of users, devices, and locations touching sensitive resources has multiplied — and every one of those connections widens the attack surface. Unsecured remote access is now one of the most direct paths into an organization’s network and can increase the risk of data breaches, which is why controlling it has become a core cybersecurity priority rather than an afterthought.
According to the National Institute of Standards and Technology (NIST): “Providing external access to internal-only resources such as sensitive servers will expose them to new threats and significantly increase the likelihood that they will be compromised. Each form of remote access that can be used to access an internal resource increases the risk of that resource being compromised.”
Therefore, regulators and cyber-insurers increasingly expect demonstrable control over who can reach critical systems remotely. Consider this: many of the highest-profile breaches began, not with a sophisticated exploit, but with an unmonitored remote connection that was simply left open.
Done well, secure remote access delivers clear business value: employees, vendors, and field teams stay productive from anywhere without friction; organizations reduce travel and on-site costs; and consistent, auditable access controls support compliance with the frameworks that govern regulated industries.
Common Security Risks of Remote Access
When remote access is left uncontrolled, several recurring risks emerge (listed below). Understanding them is the first step toward closing the gaps, because each maps to a specific control in a secure remote access strategy.
Expanded and Unmonitored Attack Surface
Every remote connection is a potential entry point. Without monitoring and segmentation, attackers can move laterally once inside.
VPN Vulnerabilities and Misconfigurations
Over-broad VPN access, stolen VPN credentials, and misconfigured gateways are among the most common breach vectors, precisely because they grant so much trust at once.
Credential Theft, Phishing, and Malware
Stolen credentials, phishing, and malware all exploit remote access paths to reach internal systems while appearing to be legitimate users.
Human Error and Unmanaged Devices
Weak passwords, unpatched personal devices, and simple misuse turn remote access into a liability — a particular challenge where unmanaged or BYOD endpoints cannot run traditional agents.
Watch this webinar on-demand: See how SRA can help you avoid these risks with Forescout experts – including our head of research at Vedere Labs, Dr. Daniel dos Santos.
Elements You Need to Ensure Strong Security
Organizations need a practical way to align secure remote access with how each site operates and who needs access. As a result, a solution needs to provide the following critical elements:
Brokered Access
This is a security model that keeps user endpoints away from critical systems. Key features include network isolation to prevent direct endpoint-to-network connections; browser-based sessions to deliver zero-footprint access; and IT/OT security to control vendor and admin access.
Zero-Footprint Access
As a major element of brokered access, zero-footprint access leverages browser-based connectivity without requiring traditional VPNs or endpoint clients. This reduces device configuration friction for third-party vendors and remote workers and minimizes the attack surface on end-user machines by preventing persistent remote access footholds. It also integrates with Zero Trust architecture policies to safely govern dynamic environment boundaries.
Credential Vaulting
This advanced technology focuses on hiding administrative or privileged credentials from users while granting them necessary system access. It is most effective when part of a secure remote access system that is paired with a privileged access management (PAM) system.
Session Monitoring
Records remote activity for oversight, investigation, and audit evidence. Such solutions provide security teams with real-time visibility, automated oversight, and even video recordings of remote user and third-party vendor activities to enforce Zero-Trust access.
Context Awareness
Connects remote activity to assets, processes, and risk in real time. Instead of merely relying on static IP addresses or basic MAC addresses, organizations gain real-time, deep contextual data to make precise security decisions.
Secure Remote Access for OT and Critical Infrastructure
Operational technology (OT) and industrial control system (ICS) environments raise the stakes for secure remote access. In these settings, availability outranks everything, because a downed production line can cost millions of dollars per hour — and many assets are legacy systems that cannot be patched, aggressively scanned, or taken offline. That makes governed, low-impact remote access essential. Vendors, system integrators, and field engineers all need connectivity to keep operations running. Yet, traditional VPNs and jump servers were built to extend networks, not to control what happens once someone is inside.
Protecting RDP, SSH, and VNC Sessions to OT Assets
Industrial assets are often reached over RDP, SSH, or VNC. A secure remote access approach brokers and records these sessions and enforces least-privilege scope. This enables vendors and engineers to do their work without those protocols being exposed directly to the internet.
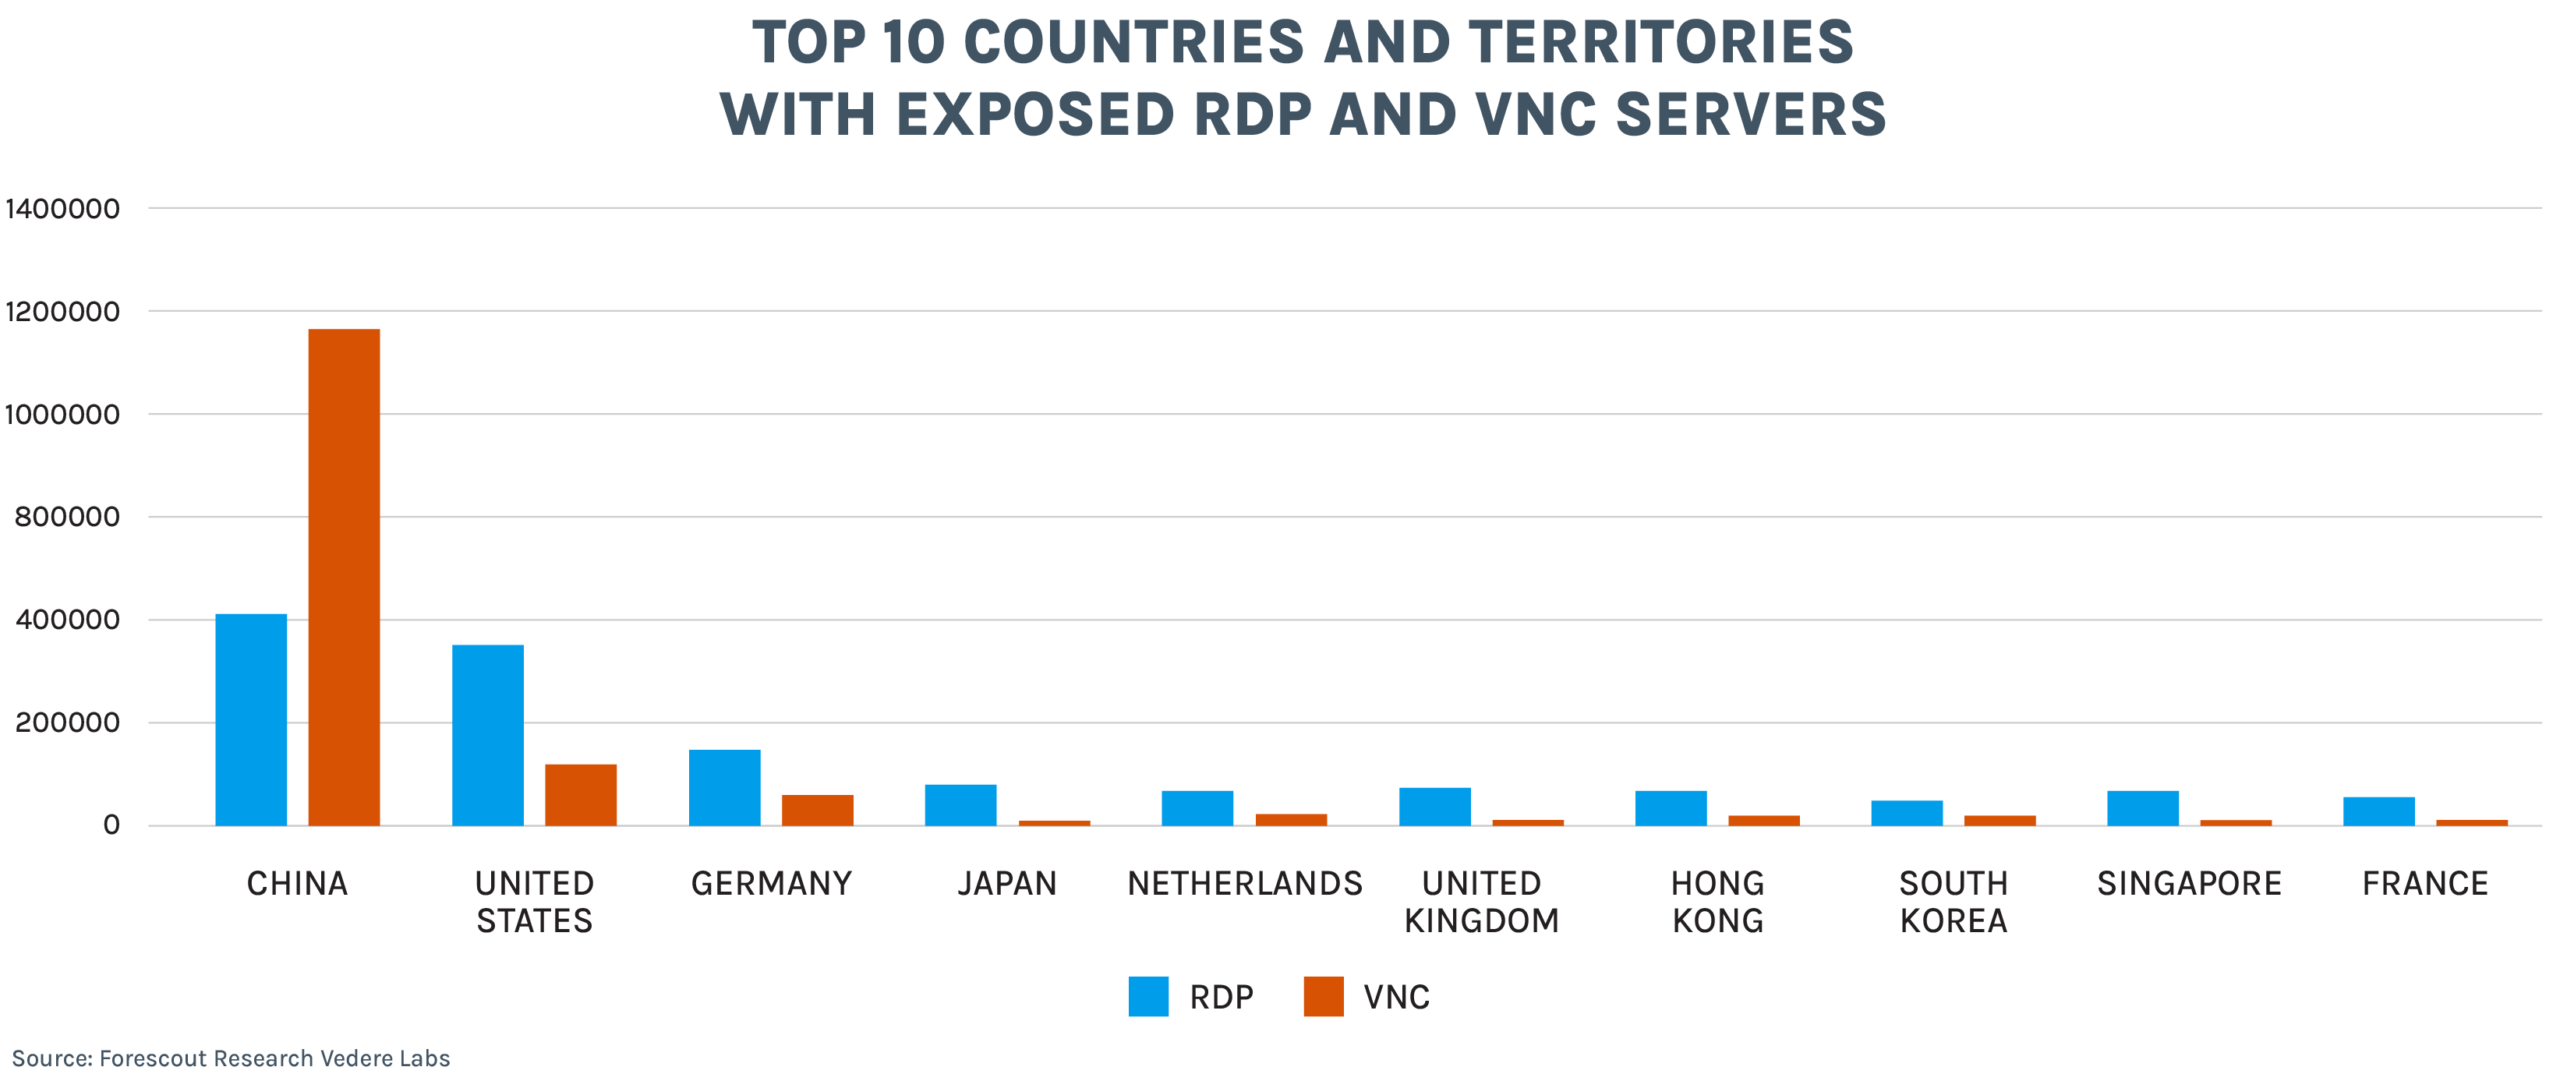
RDP and VNC continue to be risky entry points in industrial environments. Forescout’s Vedere Labs reported 1.8 million RDP and 1.6 million VNC servers are exposed on the internet. China accounts for 22% of exposed RDP and 70% of exposed VNC servers; the U.S. accounts for 20% and 7%; Germany accounts for 8% and 2%.
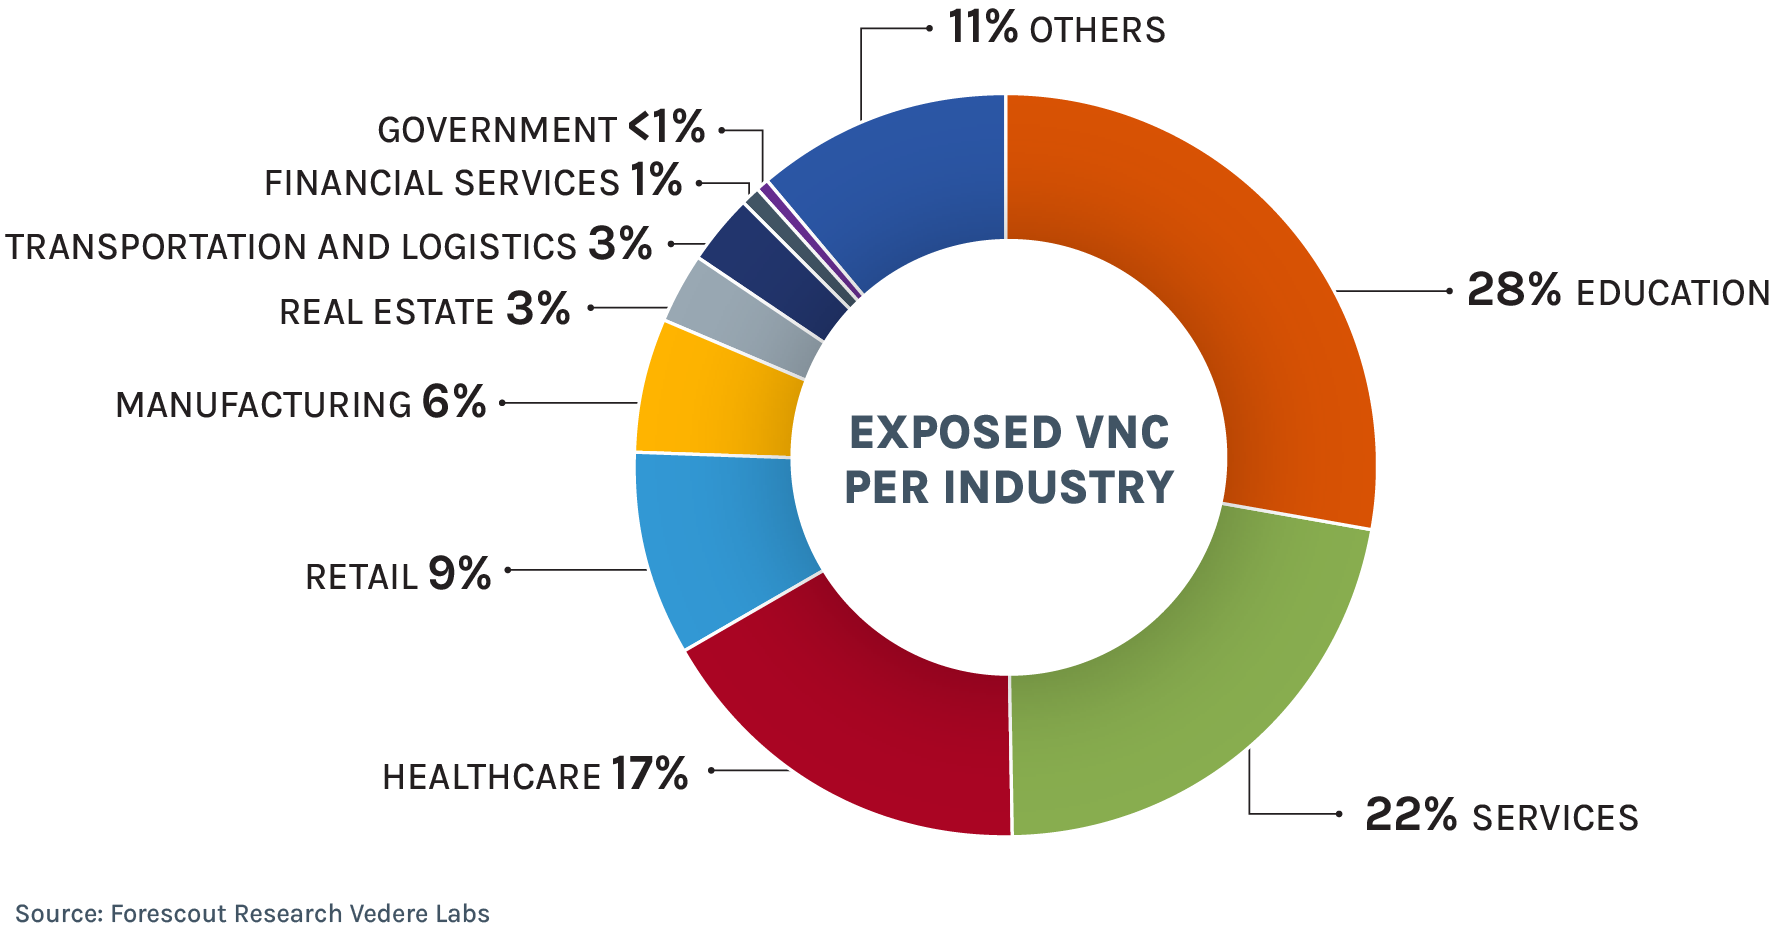
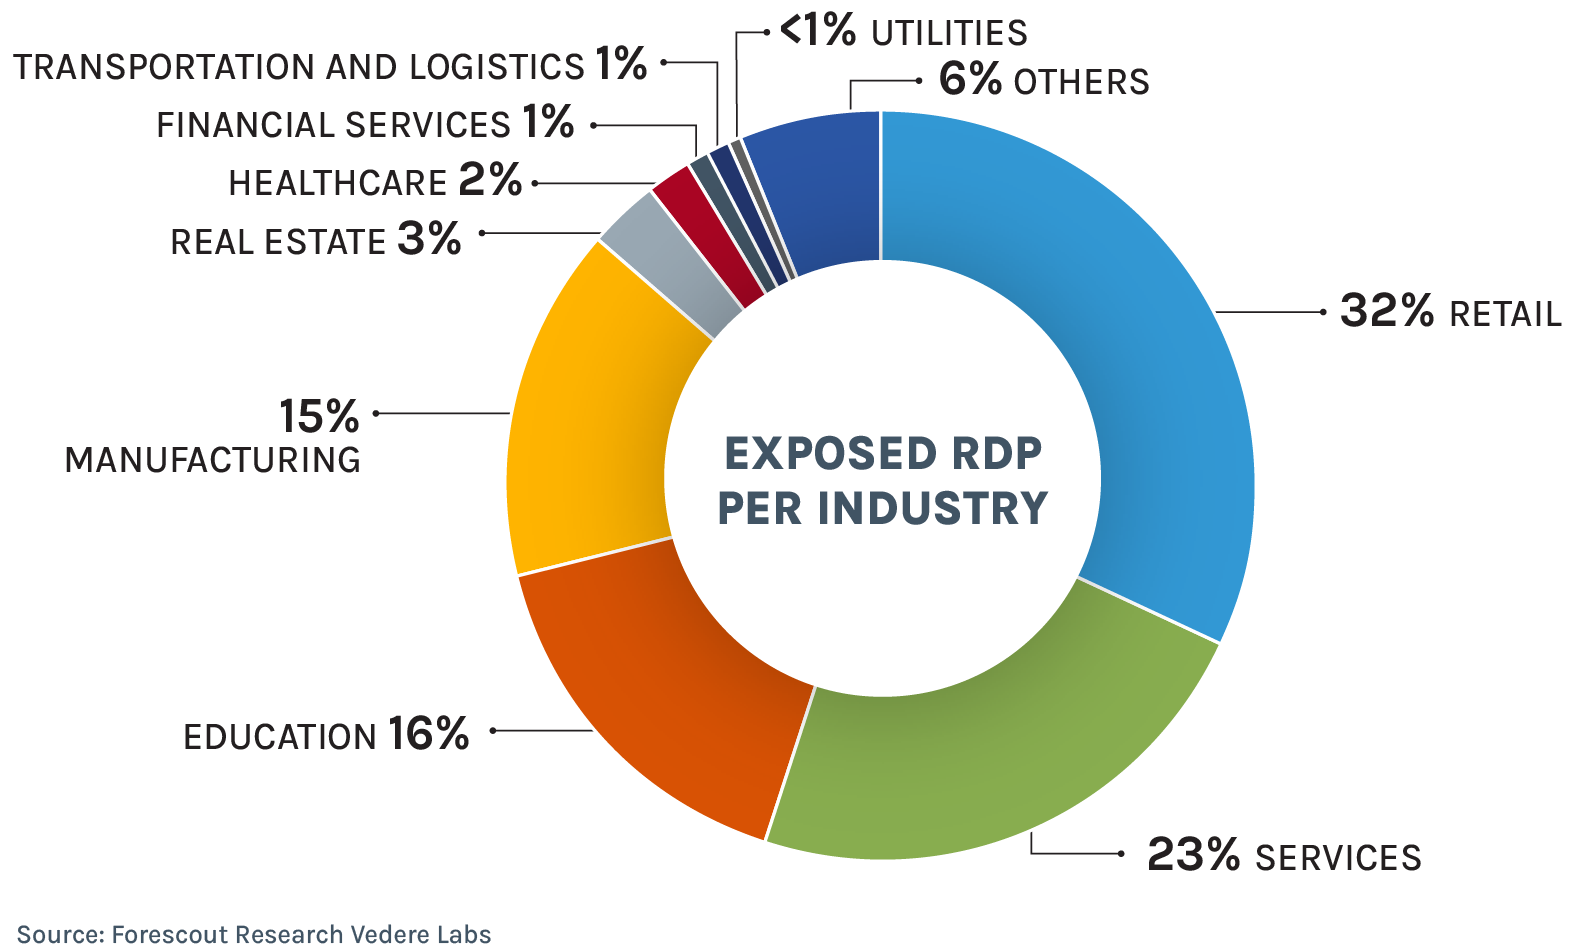
The same research isolated RDP and VNC exposure by global industry segment as well:
Faster Incident Response and Reduced On-Site Maintenance
Governed remote access allows specialists to diagnose and resolve issues quickly from anywhere. This speeds incident response for distributed critical-infrastructure sites and cuts the travel and on-site maintenance associated with downtime.
Requirements and Best Practices for OT Remote Access
OT remote access should be deployment-safe in production, avoid disruptive active scanning, cover industrial protocols, and apply zero-trust, identity-verified access with full session visibility and audit.
How to Choose a Secure Remote Access Solution
The right solution depends on who needs access, what systems they need to reach, and how sensitive those systems are. A robust shortlist shares a common set of capabilities and operational fit.
Features and Capabilities to Evaluate
When comparing solutions, look for a consistent set of capabilities:
- Strong authentication, including MFA and single sign-on
- Least-privilege, application-level access (ZTNA-style) rather than broad network access
- Encryption of all sessions
- Device posture and compliance checks before access is granted
- Session monitoring, recording, and automated response
- Broad protocol support, including RDP, SSH, and VNC
- Integration with your existing identity, security, and monitoring tools
Deployment Speed and Compliance Considerations
Weigh how quickly the solution can be deployed — especially for critical-infrastructure sites where change windows are tight. In addition, confirm that it supports the compliance frameworks your industry requires, with the audit trails to prove it!
Best Practices for Secure Remote Access
Strong technology works best alongside disciplined habits. Organizations and individual users can strengthen remote access with a few consistent practices:
- Keep devices patched and operating systems up to date
- Use strong, unique passwords and a password manager
- Enable multi-factor authentication on all corporate accounts
- Avoid public Wi-Fi for sensitive work; use a trusted or corporate connection
- Run endpoint security software and use encrypted storage
- Apply least-privilege access for employees and third-party vendors alike
- Provide security-awareness training for both employees and vendors
How Forescout Helps
Forescout SRA replaces broad remote connectivity with a controlled access layer that governs how users connect to critical systems, what they can reach, and what can happen during each session. The solution supports on-prem, cloud, and hybrid deployments with options for appliances, virtual machines, and containers on existing hardware. This flexible approach to secure remote access supports different users, use cases, and operational requirements.
Key elements of Forescout SRA:
- Brokered Access: Keeps user endpoints away from critical systems.
- Zero-Footprint: Delivers browser-based access without the need for VPN or endpoint clients
- Credential Vaulting: Keeps privileged credentials hidden from users.
- Session Monitoring: Records remote activity for oversight, investigation, and audit evidence.
- Context Awareness: Connects remote activity to asset, process, and risk in real time.
Forescout SRA provides numerous benefits beyond traditional secure remote access solutions, because it enables you to:
- Expose hidden access
- Govern the full workflow
- Control, isolate, and monitor sessions
- Gain full CPS (OT) context and understanding
Forescout SRA is available as a standalone solution or as part of the broader Forescout Vistaro™ platform. Each option adds a different layer of capability, so your organization can align secure remote access to your current needs and expand from there. You can progress from secure remote access and isolated control to platform-scale execution.
Frequently Asked Questions
What is the difference between VPN and ZTNA?
A VPN creates an encrypted tunnel that gives broad network access once a user connects. ZTNA grants granular, identity-verified access to specific applications and continuously re-verifies the session, so users never receive more reach than the task requires. For most organizations, ZTNA is the more secure default for new access, while VPNs are increasingly reserved for legacy scenarios.
How does secure remote access improve productivity?
It lets employees, vendors, and field teams work securely from anywhere without cumbersome workarounds. In this way, a distributed workforce stays productive while security controls run in the background. Removing friction from secure access also reduces the temptation to rely on risky, unsanctioned workarounds.
Can secure remote access work with legacy systems?
Yes. Modern secure remote access brokers connections to legacy and OT systems over protocols like RDP, SSH, and VNC and can secure assets that are unable to run agents, without requiring changes to those systems. This is especially valuable in OT environments, where legacy controllers and industrial equipment often cannot be updated or fitted with security agents.
What are the costs of implementing secure remote access, and how do I measure ROI?
Costs vary by number of users, deployment model, and integrations. However, you can measure ROI through reduced breach risk, lower travel and on-site maintenance, faster incident response, and the compliance savings that come from auditable access. Because a single prevented incident can outweigh years of licensing cost, ROI is usually framed around risk reduction and operational efficiency, not just price alone.
Can secure remote access work across multi-cloud environments?
Yes. Cloud-delivered approaches such as ZTNA and SASE extend consistent secure-access policy across multiple clouds and on-premises resources from a single control point.
How do I secure my device for remote access?
Keep the operating system patched, use strong unique passwords with MFA, avoid public Wi-Fi for sensitive work, and run endpoint security software with encrypted storage.