Blog
Exploiting Serial-to-Ethernet Converters in Critical Infrastructure
Forescout Vedere Labs uncovers 22 new vulnerabilities from two serial to Ethernet converter makers. See what was discovered and how to mitigate.
Since unveiling R4IoT, Forescout launched our own threat detection and response solution, Forescout XDR, part of the Forescout Platform. The following video tells the full story of what an R4IoT attack looks like and how Forescout XDR can work with your other security tools, including almost any endpoint detection and response (EDR) solution, to detect a cross-device attack like R4IoT as it unfolds, alert the SOC of a true threat and initiate policy-based remediation.
If you’re confused about cybersecurity tools and product categories, join the club. Security market confusion is a major side effect of years of increasingly sophisticated security threats and vendor innovation designed to prevent and respond to them. Add to that the growing use of AI and machine learning by both attackers and defenders and you […]
In mid-August, U.S. national security advisor Jake Sullivan sent a memo to cabinet secretaries of agencies outside the Pentagon dinging them for not complying with deadlines and steps in the 2021 Executive Order 14208 on Improving the Nation’s Cybersecurity. In doing so, he set a new timeclock ticking for submitting a detailed implementation plan by […]
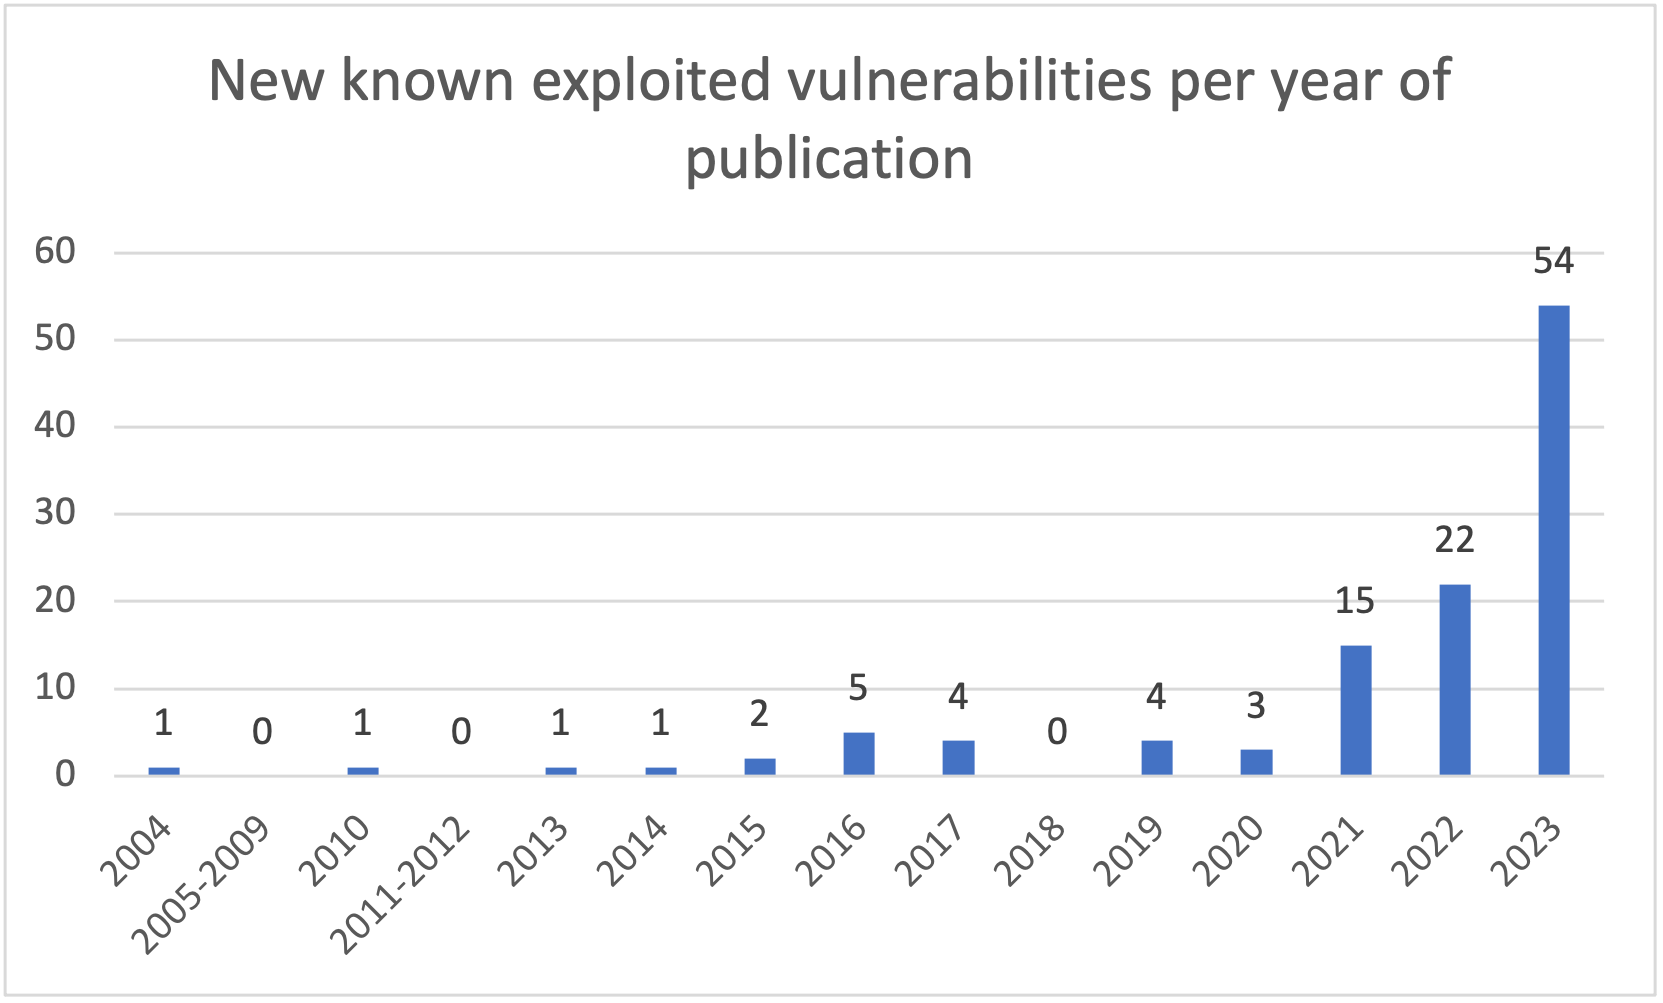
In a new threat briefing report, Forescout Vedere Labs looks back at the most relevant cybersecurity events and data between January 1 and July 31, 2023 (2023H1) to emphasize the evolution of the threat landscape. The activities and data we saw during this period confirm trends we have been observing in our recent reports, including […]

Just 60 days into my tenure as head of worldwide channel sales for Forescout, I’m pleased to unveil our new Gold Standard Partner Incentive Program, which I believe reflects best-in-class practices for rewarding channel partners with cold hard cash when you bring your most significant deals to Forescout. Namely, we will pay channel partners up […]
Cyber threats do not always come from outside an organization. Insiders, including current and former employees, contractors and other business partners with authorized access to your network, systems or data can pose significant risk, damage your reputation or even cause financial losses and business disruption. Insider threat incidents are on the rise and organizations affected […]
The Rhysida ransomware as a service (RaaS) group was first revealed in May 2023. Since then, the group has claimed 41 victims, including some high-profile ones such as the Chilean army and five educational institutions in the U.S. The group is also suspected to be behind the attack against Prospect Medical Holdings, which affected 17 […]
On July 24, a group of researchers at Midnight Blue announced TETRA:BURST, a set of five new vulnerabilities affecting the TETRA standard for radio communication. The vulnerabilities, at least one of which is an intentional backdoor, allow attackers to intercept and inject radio traffic used in a variety of settings, such as voice communication for […]
We recently published a blog post detailing how threat actors could leverage AI tools such as ChatGPT to assist in attacks targeting operational technology (OT) and unmanaged devices. In this blog post, we highlight why healthcare organizations should be particularly worried about this. First, the exploit we used in the previous example affects a vulnerability […]