Blog
Exploiting Serial-to-Ethernet Converters in Critical Infrastructure
Forescout Vedere Labs uncovers 22 new vulnerabilities from two serial to Ethernet converter makers. See what was discovered and how to mitigate.
Identity is foundational for Zero Trust, but it’s not the final authority. Here, we explore why context is needed to fully realize trust in security programs.
The United States is in a race to develop its quantum capabilities and to migrate critical systems to post-quantum cryptography before standard encryption practices become obsolete. That’s because AI is merging with quantum computing and rapidly accelerating the timeline to Q-day. Frontier models can allow technologists to identify more efficient ways to design, architect, and […]
Forescout supports the NVIDIA Open Agent Safety Platform, bringing out-of-band, in-silicon monitoring to AI agents in critical environments.
Encryption risk in manufacturing is real. Here are the questions about PQC you need to ask with guidance on how to limit your quantum risk.
What CISA and the Five Eyes want from your secure remote access for OT, and how Forescout SRA and the Forescout Vistaro platform get you there.
The recent Hugging Face incident has been widely discussed as an AI safety story. Public reporting focused on the notion that increasingly capable AI systems were able to identify and exploit vulnerabilities, expand their access beyond intended boundaries, and ultimately reach external systems. That framing is understandable because it touches on questions that have long […]
In the Agentic-AI era, security decisions still depend on network fundamentals grounded in complete device intelligence and trusted guardrails.
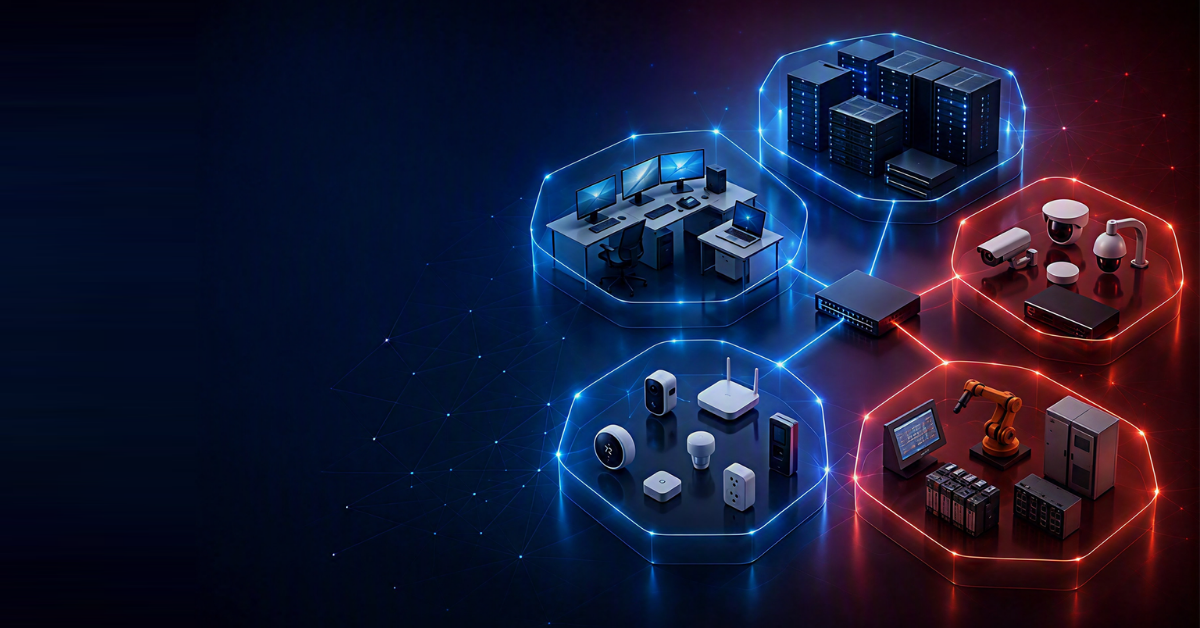
Forescout Research studies the security of network segmentation architecture from 209 organizations, 47,000 segments, and 2.5 million devices.
Forescout’s Perspective on The Forrester Wave™: Operational Technology Security Solutions, Q3 2026 One could argue that the biggest message from this Forrester Wave report is that the market has reached its next phase. The first phase of OT security was asset discovery. The second phase was threat detection. And we’re now entering phase three: operational […]