eBook
The Benefits of Network Monitoring for Industrial Digitalization

Industrial Digitalization
Today, manufacturing is powered by thousands of connected devices, massive computing power and artificial intelligence. These advances enable manufacturers to adopt flexible, built-to-order production methodologies that include automated workflows and real-time performance monitoring. Together they improve efficiency, reduce errors and cut costs, but with these benefits comes increased cyber risk.
Industrial digitalization is characterized by the integration of computation, networking and physical processes, which bring clear business advantages. It has also led to highly complex, heterogeneous manufacturing networks due to the convergence of enterprise and manufacturing assets and increased use of Internet of Things (IoT) devices. As a result, manufacturers are operating with increased cybersecurity and operational risk that can lead to downtime if they are not top-of-mind in a holistic cybersecurity and digital transformation strategy.
Threats and Needs
In 2023, a leading boating manufacturer, Brunswick, fell victim to a cyber attack that caused its operation to be down for nine business days causing losses of $13 million. The company was forced to stop operations in some locations while experts and law enforcement dealt with the incident. While ransomware was not officially blamed, security experts believe it to have been the case.
The knock-on effect of cyber attacks on the supply chain cannot be underestimated. In 2023, semiconductor maker, Applied Materials, had a very similar security event occur in its supply chain when its supplier, MKS Instruments, was targeted in an attack. Applied Materials said it cost the company upwards of $250 million from the incident.
However, cyberattacks are by far not the most imminent threat to the manufacturing industry. Despite the noise from the media, the likelihood of a successful attack against industrial control systems (ICS) is relatively low. On the contrary, cyber incidents happen daily. They include small to major network or process disruptions due to misconfigurations, erroneous commands and operations, software errors and device failures – none of them intentional, but nevertheless all impacting the asset owner’s bottom line.
To effectively protect the network and avoid downtime, asset owners must be able to detect all these threats in a timely manner. When choosing a strategy to implement, guidelines such as the NIST Cybersecurity Framework and IEC 62443 can provide valuable advice on how to improve the overall cybersecurity of industrial networks.
The figure on page 4 provides a good overview of the industrial automation threat landscape, including the frequency and impact of threats and problems. These operational and networking threats are detected daily at most of our manufacturing customers.
Operational Resilience Under Pressure
Understanding the Real Threats to Your Business Integrity

Cybersecuirty
- Ransomware
- Targeted & Zero-Day attacks
- Industrial espionage
- Insider threats
- Firewall misconfiguration
- Use of insecure devices, protocols and services
Frequency: Yearly
Impact: $$$$$
Networking
- Unstable & broken links
- Commands that do not reach the destination
- Misconfiguration of network services
- “Noisy” devices causing traffic floods
Frequency: Weekly-Monthly
Impact: $$$
Process Operations
- Misconfigured and malfunctioning devices
- Device failure and downtime
- Non-compliant data exchange
- Undesired maintenance activity
- Process instability and anomalies
Frequency: Daily-Weekly
Impact: $$
Compliance as an Opportunity: Transforming Risk into Resilience
Today’s manufacturing is a constant race to be faster, smarter, and more connected, to stay competitive and ahead of the curve. But all it takes is one small cyber hiccup to bring everything to a halt. To thrive in this complex threat landscape, in addition to speed and connectivity, a business needs the ability to absorb a hit and keep moving forward. Organizations can transform compliance from a regulatory burden into a driver of smarter decisions, enabling them to identify and address issues early, before they escalate into costly incidents.
To build that kind of operational resilience, organizations need a clear plan and a practical framework to follow. The NIST Cybersecurity Framework (CSF) offers exactly that, core functions and recommendations that help establish visibility, enforce control, and improve response across the industrial environment.
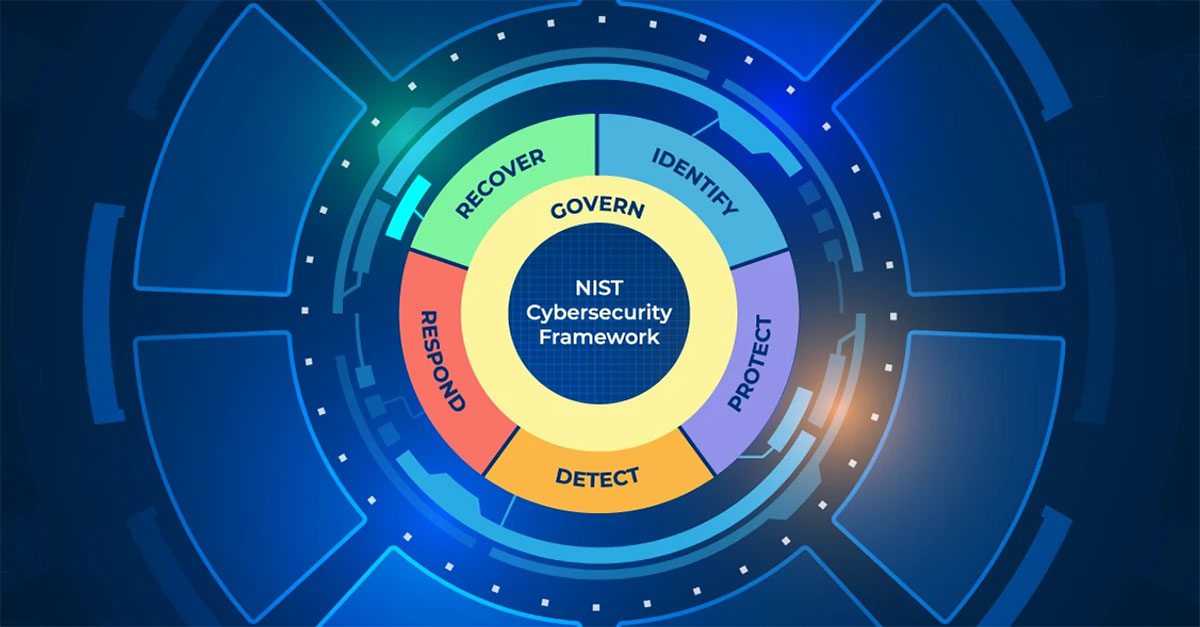
Govern
The Forescout Vistaro™ platform gives organizations comprehensive across all device types and Purdue levels closing gaps and reducing blind spots across teams and environments. With this broad coverage and easy integration into the existing security stack, we streamline the design and enforcement of cybersecurity policies across the entire industrial infrastructure. We provide the insights you need to track risk exposure, measure progress with clear KPIs, and support accountability across both technical teams and business leadership.
- Enterprise-wide visibility across IT, OT, IoT, and BAS with 30+ active and passive discovery methods, adaptable to any environment.
- Flexible deployment options to meet diverse operational needs and maturity levels, from cloud to image containers, including support for air-gapped or highly segmented networks.
- Seamless integration with the existing security stack, acting as a force multiplier rather than another siloed tool.
- Centralized policy management engine to define, enforce, and audit cybersecurity policies across all asset types, technologies and networks.
- Unified view of IT and OT risk with built-in KPIs and AI-enhanced reporting to support governance, accountability, and strategic decision-making.
Identify
When threats hide in blind spots, visibility becomes your first line of defense to identify vulnerabilities and exposures. Forescout builds and maintains a real-time inventory of assets, systems, and services across IT and OT environments, mapping communications, exposing dependencies, and tracking changes over time. Powered by proprietary threat intelligence and a combined security and operational risk score, the Vistaro™ platform makes identifying exposure and prioritizing remediation by impact or exploitability faster and more effective.
- Native support for IT and OT systems, both managed and unmanaged, eliminates silos, reduces hidden threats, and avoids costly third-party integrations, data duplication and false positive.
- Combined security and operational risk scoring provide a more accurate view of exposure based on impact, likelihood, and business criticality.
- Enriches asset and threat data through integration with third-party tools, enhancing vulnerability detection, tracking configuration changes, and monitoring device risk posture over time.
- Leverages over 150 classification attributes to build a more accurate view of asset risk, streamline remediation, and share enriched insights in real time across your security ecosystem.
- Retains historical risk data to support compliance reporting, monitor security trends, and provide evidence for KPIs and audit requirements.
Protect
How can you secure what you can’t control? As connected assets grow and identities move beyond traditional boundaries, organizations need more than a static approach. Forescout enables dynamic, policy-based control over access, identity, and behavior, making sure that only trusted users and devices can interact with critical systems. This real-time enforcement enhance data protection, supports least-privilege access, and builds the foundation for a resilient, zero-trust architecture. Most importantly, it works with your existing security stack, maximizing current investments while extending control across the entire enterprise.
- Identity and access management with risk-based policies, dynamic segmentation, and least-privilege principles to limit exposure and lateral movement.
- Asset and communication baseline with continuous posture and compliance validation to monitor behaviour, configuration, and integrity changes that could indicate compromise or policy drift.
- Zero trust segmentation and data flow visibility to restrict access based on trust boundaries and detect unauthorized communication, exfiltration attempts, or policy violations.
- Device lifecycle management to track configuration changes, block unauthorized software, and enforce security baselines across asset types.
- Infrastructure monitoring, configuration, bandwidth, system load, and resource usage to identify weak spots, operational issues and improve resilience.
- Security stack integration and orchestration to enforce policies and trigger automated remediation through existing tools and workflows.
Detect
Finding and analyzing cyber threats requires more than passive monitoring, it demands broad visibility, deep context, and precise classification. Unlike OT-only security tools, Forescout delivers enterprise-wide detection coverage across IT, OT, IoT, and BAS by correlating over 200 different data sources. Combined with deep packet inspection, anomaly detection, and proprietary threat intelligence from Vedere Labs, the platform uncovers hidden threats others miss and gives security teams the clarity to act faster and with confidence.
- Intelligence-driven detection powered by deep packet inspection, anomaly detection, and proprietary threat intelligence from Vedere Labs to identify known and unknown threats across IT and OT.
- Event classification and triage using high-fidelity data, filters, customizable rules, and detailed asset context to reduce false positives and streamline analyst workflows.
- Assisted response for OT with 24/7 expert support, threat analysis, and remediation guidance tailored to industrial environments.
- Runtime extensibility to fine-tune detection logic, integrate custom IoCs and IoAs, and adapt to evolving threats or operational edge cases.
Respond
For many organizations, incident response is still a slow, manual, and fragmented process, relying on overloaded teams to piece together actions across disconnected systems. As threats move faster, and environments grow more complex, even wellfunded security teams struggle to keep up. Forescout shifts response from reactive to proactive, orchestrating and automating containment, remediation, and escalation across your existing security tools. The result: faster incident resolution, reduced downtime, and a stronger security posture, without increasing headcount.
- End-to-end incident response workflow that spans detection, analysis, containment, and recovery, executed from a single, integrated platform.
- Automated response orchestration across your existing IT and security tools to accelerate remediation, reduce manual effort, and ensure consistent execution.
- Detailed incident timelines and root-cause analysis, backed by asset history, PCAPs, and data retention for foresting investigation, reporting and compliance.
- Built-in prioritization and classification based on tactics, techniques, and procedures (TTPs) to focus resources on the most critical and highest-impact threats.
Recover
Restoring operations after an incident isn’t just about turning systems back on, it’s about making sure everything is restored safely and without residual risk. The Forescout Vistaro™ platform helps organizations validate the integrity of assets and systems post-recovery by providing access to detailed historical data, configuration baselines, communication flows, and behavioral patterns. This visibility supports comparison against known-good states, helping teams assess the success of recovery efforts, validate backup systems, and prevent reinfection.
- Baseline and historical insight into asset configurations communications and dependencies to verify system integrity, detect deviations.
- Recovery validation with comparison of restored environments with known-good baselines, system performance and behaviour and identification of anomalies or gaps.
Why Choose Forescout
The Forescout Vistaro™ platform provides complete asset intelligence and control across IT, OT, IoT, and IoMT environments. For more than 20 years, Fortune 100 organizations, government agencies, and large enterprises have trusted Forescout as their foundation to manage cyber risk, ensure compliance, and mitigate threats with seamless context sharing and orchestration across more than 180 fully featured security and IT product integrations. With Forescout, every cybersecurity investment is more effective.